CYBER SECURITY CONSULTING SERVICE AWARDS AND RECOGNITIONS
CyberSecOp's comprehensive managed security services, cyber security consulting, professional services, and data protection technology are recognized as industry-leading threat detection and response solutions by major analyst firms, key media outlets, and others.
What Does a Security Compliance Consultant Actually Do?
Every industry has its own version of the same question: are we compliant? Healthcare organizations ask it about HIPAA. Financial institutions ask it about PCI-DSS and SEC requirements.
Every industry has its own version of the same question: are we compliant? Healthcare organizations ask it about HIPAA. Financial institutions ask it about PCI-DSS and SEC requirements. Technology companies ask it about SOC 2. Government contractors ask it about CMMC. The honest answer, for most businesses, is: we are not entirely sure. That uncertainty is precisely why security compliance consultants exist.
A security compliance consultant helps organizations understand which regulatory and industry frameworks apply to them, identify the gaps between their current security posture and those requirements, implement the controls necessary to close those gaps, and produce the documentation that proves compliance to auditors, regulators, and clients. The role sits at the intersection of cybersecurity, regulatory expertise, and operational change management, and it is one of the most practical investments a business can make. CyberSecOp's Compliance Security Consulting practice delivers this expertise across the full range of frameworks that affect businesses in regulated and high-risk industries.
What a Security Compliance Consultant Is Not
Before explaining what security compliance consultants do, it helps to clear up a common misconception. A compliance consultant is not simply a policy writer who produces documents for an audit and moves on. That approach, sometimes called compliance theatre, produces documentation that satisfies a checklist without improving actual security. The results are organizations that pass audits and still suffer breaches, because the controls on paper were never implemented in practice.
Effective security compliance consulting is grounded in real security operations. Policies must reflect actual system configurations. Controls must be tested, not described. Audit evidence must be drawn from live environments. A consultant who cannot assess the technical reality of your security controls cannot tell you whether you are genuinely compliant, only whether your paperwork looks compliant.
The Frameworks a Security Compliance Consultant Works Across
Compliance requirements vary significantly by industry, geography, and the type of data an organization handles. A security compliance consultant needs fluency across multiple frameworks, because most organizations are subject to more than one simultaneously.
HIPAA, Healthcare and Business Associates
The Health Insurance Portability and Accountability Act imposes security requirements on covered entities, healthcare providers, health plans, and healthcare clearinghouses, and on the business associates that handle protected health information on their behalf. HIPAA's Security Rule specifies administrative, physical, and technical safeguards that must be in place for electronic PHI, along with documentation requirements and risk analysis obligations. CyberSecOp's healthcare security consulting practice works with both covered entities and business associates to implement HIPAA-compliant security programs and prepare for Office for Civil Rights audits.
PCI-DSS, Payment Card Environments
The Payment Card Industry Data Security Standard applies to any organization that stores, processes, or transmits cardholder data. PCI-DSS is structured around twelve core requirements, covering network security, access control, vulnerability management, monitoring, and policy, with specific technical controls required at each merchant level. Non-compliance exposes organizations to fines, increased transaction fees, and potential loss of the ability to process card payments. CyberSecOp's PCI compliance assessment services help organizations understand their cardholder data environment, scope their compliance obligations accurately, and implement the technical controls that PCI-DSS requires.
NIST Cybersecurity Framework
The National Institute of Standards and Technology Cybersecurity Framework provides a flexible, risk-based approach to managing cybersecurity risk across five core functions: Identify, Protect, Detect, Respond, and Recover. The NIST CSF is used as a compliance baseline by federal agencies, government contractors, and increasingly by private-sector organizations seeking a structured approach to security program development. CyberSecOp's NIST compliance and NIST security assessment services help organizations map their current controls against the framework, identify maturity gaps, and build the roadmap to achieve their target profile.
SOC 2, Technology and Service Organizations
System and Organization Controls 2 (SOC 2) is a framework developed by the American Institute of Certified Public Accountants for technology companies and service providers that handle customer data. SOC 2 evaluates controls across five Trust Service Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. A SOC 2 Type II report requires demonstrating that controls were not just in place but operating effectively over a defined audit period. CyberSecOp's security audits and compliance consulting practice supports organizations through SOC 2 readiness assessments, control implementation, and audit preparation.
CMMC, Defence Industrial Base
The Cybersecurity Maturity Model Certification framework applies to organizations in the defense industrial base that handle Controlled Unclassified Information or Federal Contract Information. CMMC 2.0 is structured across three levels, with Level 2 mapping to the 110 security requirements of NIST SP 800-171. CyberSecOp's CMMC consulting services help defense contractors assess their current posture against CMMC requirements, implement required controls, and prepare for the formal assessments that DoD contracts increasingly mandate.
ISO 27001, GDPR, and Other Frameworks
Beyond the US-centric frameworks above, many organizations must address ISO 27001 certification requirements, GDPR obligations for personal data handled on behalf of European individuals, NYDFS cybersecurity regulations, or industry-specific requirements in financial services, energy, and healthcare. CyberSecOp's compliance consulting practice spans ISO 27001, GDPR, and NYDFS, providing a single point of expertise across multi-framework compliance environments.
How a Security Compliance Engagement Is Structured
Understanding what a compliance consultant does is clearest through the structure of an actual engagement. While the specifics vary by framework and organizational context, most compliance consulting engagements follow a consistent pattern.
Phase 1: Scoping and Discovery
The engagement begins with scoping, establishing exactly which regulatory requirements apply to the organization, which systems and processes fall within the compliance boundary, and what the current state of security controls looks like. This involves reviewing existing policies and procedures, interviewing key personnel across IT, legal, HR, and operations, and conducting a technical inventory of the systems, data flows, and third-party relationships that are relevant to the compliance program.
Scoping is often where organizations first encounter the breadth of their compliance obligations. A healthcare technology company, for example, may be simultaneously subject to HIPAA for PHI it processes, PCI-DSS for payment transactions, and SOC 2 for the enterprise clients evaluating its security posture. A consultant who understands how these frameworks overlap, and where a single control satisfies multiple requirements, can design a program that is comprehensive without being redundant.
Phase 2: Gap Assessment
A gap assessment maps the organization's current security posture against the requirements of the applicable framework or frameworks. Each required control is evaluated against what is actually in place, not what the policy says should be in place, but what the technical configuration, operational practice, and documented evidence demonstrate. CyberSecOp's cybersecurity assessment services produce a detailed gap report that identifies each deficiency, rates it by risk level, and provides a prioritized remediation roadmap.
Phase 3: Remediation and Control Implementation
This is where the practical security work happens. Depending on the gaps identified, remediation may involve implementing technical controls, deploying multi-factor authentication, configuring encryption at rest and in transit, establishing logging and monitoring infrastructure, as well as operational changes such as formalizing change management processes, establishing vendor risk assessment procedures, and implementing security awareness training programs.
CyberSecOp's compliance consultants do not simply advise on what needs to be done, they work alongside internal IT and security teams to implement controls, configure systems, and validate that requirements are genuinely being met. Integration with CyberSecOp's managed security services can provide the ongoing monitoring and operational security capabilities that many frameworks require.
Phase 4: Documentation and Evidence Collection
Compliance is demonstrated through documentation. Policies, procedures, risk assessments, vendor agreements, training records, system configuration evidence, and audit logs must all be organized, current, and accessible. A security compliance consultant structures this documentation in a way that maps directly to the framework requirements, so that when an auditor asks for evidence of a specific control, the right documentation is immediately available.
For organizations pursuing formal certifications or regulatory audits, the consultant also prepares personnel for the audit process itself, coaching staff on how to respond to auditor inquiries, reviewing the evidence package before submission, and managing any findings that emerge during the audit.
Phase 5: Ongoing Program Maintenance
Compliance is not a destination, it is a continuous state that must be maintained as the organization's systems, personnel, and threat environment change. Most frameworks require annual assessments, regular risk reviews, and ongoing evidence of control effectiveness. CyberSecOp's Virtual CISO program provides the ongoing security leadership that keeps compliance programmes current between formal audit cycles, ensuring that control changes are documented, new risks are assessed, and the organization is always prepared for the next audit.
What Outcomes Should You Expect from a Compliance Engagement?
The tangible outputs of a security compliance engagement depend on the framework and scope, but clients should expect: a clear picture of their current compliance posture, a prioritized plan for addressing identified gaps, implemented controls that address the most significant deficiencies, a complete documentation package supporting audit readiness, and trained staff who understand both the requirements and their individual responsibilities within the compliance program.
Beyond the audit itself, a well-executed compliance program delivers security improvements that protect the organization against real threats, not just regulatory penalties. HIPAA's access control requirements prevent unauthorized access to patient data. PCI-DSS's logging requirements create the audit trail that enables effective incident response. NIST's detection and response requirements build the operational capability to identify and contain breaches before they become catastrophic.
Why Compliance Consulting Is Not a DIY Project
Some organizations attempt to manage compliance using internal staff who divide their time between compliance work and their primary IT or legal responsibilities. The results are predictable: compliance tasks are deprioritized during busy operational periods, framework expertise is shallow, documentation is inconsistent, and the organization either fails audits or achieves compliance on paper without the underlying security improvements that compliance is meant to produce.
A dedicated compliance consultant brings framework expertise that takes years to develop, experience with the specific evidence and control implementations that auditors require, and the bandwidth to treat compliance as a primary responsibility rather than a secondary task.
For organizations evaluating their compliance readiness, a cybersecurity assessment is the natural starting point, establishing a clear baseline before the full compliance engagement begins. CyberSecOp's compliance consulting team works across all major frameworks and industries. Contact us at cybersecop.com/contact to discuss your compliance requirements.
Network Security Consulting: How Experts Harden Your Infrastructure Against Modern Threats
Most organizations have a network security story they tell themselves. Firewalls are in place. The perimeter is protected. The IT team handles patches. The reality that a network security consultant reveals is usually more complicated, and more exposed, than that story suggests.
Most organizations have a network security story they tell themselves. Firewalls are in place. The perimeter is protected. The IT team handles patches. The reality that a network security consultant reveals is usually more complicated, and more exposed, than that story suggests. Networks grow organically, accumulating configurations, devices, and connections that were each added for legitimate reasons but that collectively create an attack surface that no one has mapped in its entirety.
Network security consulting is the discipline of systematically identifying, assessing, and remediating the vulnerabilities and architectural weaknesses in an organization's network infrastructure. It combines technical expertise in network architecture and security protocols with the threat intelligence to understand which vulnerabilities attackers are actively exploiting. CyberSecOp's network security practice delivers this capability to businesses across industries, from SMBs securing their first purpose-built security architecture to mid-market organizations hardening complex, multi-site environments.
Why Network Security Requires Outside Expertise
Internal IT teams build and maintain networks with operational efficiency as the primary objective. Security considerations are real, but they compete with uptime requirements, user experience concerns, budget constraints, and the pace of business change. The result, in most organizations, is a network that functions reliably but has accumulated security debt, configurations that made sense at the time, access policies that were never revisited, and connectivity that was granted to solve an immediate problem and never constrained after the problem was resolved.
An outside network security consultant brings two things that internal teams rarely have simultaneously: dedicated security expertise and an external perspective. They are not constrained by familiarity with how things have always been done, and they are not responsible for maintaining the operational continuity that makes security improvements difficult to prioritize internally. Their job is to see the network as an attacker would and then help the organization fix what that perspective reveals.
CyberSecOp's risk assessment services establish the baseline picture of network security posture before a consulting engagement begins, giving both the consultant and the client a shared, evidence-based understanding of where the most significant vulnerabilities lie.
What a Network Security Consulting Engagement Covers
Network Architecture Review
The foundation of any network security engagement is a thorough review of the network architecture, the topology, segmentation design, routing configuration, and trust relationships that define how traffic flows through the environment. Consultants examine network diagrams, firewall rule sets, switching configurations, and access control lists to understand what is connected to what, which systems can communicate with which others, and whether those connectivity patterns are consistent with the principle of least privilege.
Architecture reviews consistently reveal the same categories of problems. Flat networks, where all systems can communicate freely with each other, are one of the most common. A flat network means that a compromised workstation can attempt to communicate directly with financial systems, servers containing sensitive data, and critical infrastructure without encountering any technical obstacles. Segmentation that isolates critical systems and limits lateral movement is among the highest-impact security improvements most organizations can make, and it begins with understanding the current architecture.
Firewall and Perimeter Security Assessment
Firewalls are the most visible component of network security, but they are frequently misconfigured in ways that undermine their protective value. Rule sets accumulate over years as exceptions are added, temporary rules become permanent, and policies appropriate for a past network configuration persist long after that configuration changed. A network security consultant reviews the complete firewall rule set, identifies rules that are overly permissive, redundant, or inconsistent with current security policy, and produces a remediation plan that tightens access without disrupting legitimate operations.
Perimeter security assessment also covers remote access infrastructure, VPN configurations, multi-factor authentication enforcement, and the policies governing who can connect remotely and under what conditions. Remote access has expanded significantly for most organizations, and the security controls around it have not always kept pace with that expansion.
Vulnerability Assessment and Penetration Testing
Vulnerability scanning identifies known vulnerabilities in network-connected systems, unpatched software, weak configurations, default credentials, and exposed services that should not be reachable from the positions where they are accessible. CyberSecOp's threat and vulnerability assessments provide continuous, prioritized vulnerability identification across the network environment, distinguishing vulnerabilities that represent genuine, exploitable risk from the theoretical findings that occupy the tail of most scan reports.
Penetration testing goes beyond scanning to simulate the techniques that actual attackers use. A penetration test attempts to exploit identified vulnerabilities, move laterally through the network, escalate privileges, and reach the assets that represent the organization's most significant breach risk. CyberSecOp's penetration testing services provide this evidence-based assessment across network, application, and social engineering attack surfaces.
Network Segmentation Design and Implementation
Segmentation, dividing the network into isolated zones that control which systems can communicate with which other systems, is the architectural control that most limits the damage from a successful intrusion. A compromised device in a properly segmented network can communicate only with the systems it is explicitly permitted to reach. An attacker who gains a foothold in one segment cannot freely move to the servers, databases, or administrative systems that represent the highest-value targets.
Effective segmentation design requires balancing security with operational reality. Business systems need to communicate with each other. Users need access to the resources their roles require. Network security consultants design segmentation architectures that implement least-privilege connectivity, permitting what is necessary while blocking what is not, in a way that can be implemented without disrupting operations.
Wireless Network Security
Wireless networks extend the attack surface beyond the physical boundary of the building. Poorly configured wireless infrastructure, using outdated security protocols, providing guest network access that is insufficiently isolated from corporate systems, or broadcasting corporate SSIDs without adequate authentication requirements, creates exposure that a wired perimeter cannot address. Network security consulting covers wireless architecture review, protocol configuration, guest network isolation, and rogue access point detection.
Network Access Control and Identity Integration
Zero Trust security architecture begins with controlling who and what can access the network. Network Access Control systems enforce authentication requirements before granting devices access, ensuring that only managed, policy-compliant devices can connect to corporate resources, and that guest or unmanaged devices are isolated to restricted network segments. CyberSecOp's network security services integrate NAC and identity management capabilities into a coherent access control framework aligned with Zero Trust principles.
Monitoring and Detection Infrastructure
A hardened network without monitoring is a static defense against a dynamic threat. Attackers who find a way past perimeter controls need time to establish persistence, move laterally, and reach their targets, and that time is the detection window that a properly instrumented network creates. Network security consulting covers the design and implementation of monitoring infrastructure: network traffic analysis, intrusion detection systems, log collection and correlation, and alerting configuration. CyberSecOp's Security Operations Center provides 24/7 monitoring across client network environments, turning monitoring infrastructure into a detection and response capability.
The Most Common Network Vulnerabilities in SMB and Mid-Market Environments
Across network security assessments, a consistent set of vulnerabilities appears with predictable frequency. Understanding the most common findings helps organizationsidentify where their own environments are most likely to be exposed.
Flat network architecture: No segmentation between user workstations, servers, and critical infrastructure, allowing unrestricted lateral movement for any attacker who gains a foothold.
Overly permissive firewall rules: Legacy rules that allow broad access ranges, temporary rules that became permanent, and rules that were never removed after the systems they served were decommissioned.
Unpatched network devices: Routers, switches, and firewalls running firmware versions that contain known, exploited vulnerabilities, frequently because network device patching is lower priority than server and workstation patching.
Weak or absent VPN multi-factor authentication: Remote access that relies on username and password alone, making credential theft sufficient to gain direct access to the internal network.
Inadequate logging and monitoring: Log collection that is incomplete, retention periods too short for effective incident investigation, and no correlation or alerting capability to surface suspicious patterns.
Default credentials on network devices: Routers, switches, wireless access points, and management consoles still configured with manufacturer default usernames and passwords, are among the first things an attacker checks.
Exposed management interfaces: Administrative interfaces for network devices accessible from the general corporate network or from the internet, allowing any authenticated user to attempt access.
Shadow IT connectivity: Unauthorized network devices, personal routers, consumer IoT devices, unmanaged laptops, connected to the corporate network without IT knowledge or security controls.
What Changes After a Network Security Engagement
The output of a network security consulting engagement is not a report that describes problems. It is a set of implemented improvements, a segmented network architecture that limits lateral movement, a firewall rule set that permits only legitimate traffic, monitored infrastructure that creates the detection capability to identify intrusions before they reach critical systems, and documented policies that give the IT team a clear framework for maintaining the hardened configuration going forward.
The durability of these improvements depends on the quality of the implementation and the organizational commitment to maintaining configuration discipline. CyberSecOp's ongoing network security management services provide the continuous oversight that keeps hardened network configurations hardened, monitoring for configuration drift, reviewing changes before they introduce new vulnerabilities, and updating detection rules as the threat landscape evolves.
Starting the Conversation
Network security is not a problem that an organizationcan solve once and consider finished. The threat landscape evolves, the network grows, and configurations that were secure yesterday may not be secure after the next change. What a network security consulting engagement provides is the foundation, a clear picture of current exposure, a hardened architecture that limits the damage from a successful intrusion, and the monitoring infrastructure to detect threats that make it past the perimeter.
For organizations ready to understand their current network security posture, a cybersecurity assessment provides the baseline that informs a focused consulting engagement. CyberSecOp's network security consulting services are available to organizations across industries and geographies. Contact us at cybersecop.com/contact to speak with a member of our team.
Managed SOC vs. In-House SOC: Which Is Right for Your Organisation?
At some point in every organization's security maturity journey, the same question surfaces: should we build our own Security Operations Centre, or should we engage a managed SOC provider?
At some point in every organization's security maturity journey, the same question surfaces: should we build our own Security Operations Centre, or should we engage a managed SOC provider? It is a significant decision, one that touches budget, talent strategy, technology investment, and the organization's risk tolerance. And it is one that many organizations approach without a clear picture of what each option actually costs and delivers in practice.
This guide compares in-house and managed SOC options across the factors that matter most, cost, coverage, staffing, technology, scalability, and response capability, so that your organization can make an informed choice. CyberSecOp's managed SOC services are built for organizations that have worked through exactly this comparison and concluded that the managed model delivers better outcomes at lower risk.
What Is a Security Operations Centre?
A Security Operations Centre is the function responsible for continuous monitoring of an organization's security environment, detecting threats, investigating alerts, and coordinating the response to confirmed incidents. Regardless of whether a SOC is in-house or managed, it requires three things to be effective: people with the skills to identify and respond to threats, technology to collect and analyze security data, and processes that ensure consistent, repeatable response to the full range of threat scenarios an organization faces.
The performance gap between a well-resourced, mature SOC and an understaffed or poorly tooled one is enormous. A SOC that cannot investigate alerts quickly, that lacks the expertise to distinguish genuine threats from false positives, or that has no tested playbooks for common attack scenarios will routinely fail to detect or contain the threats it exists to address. CyberSecOp's Security Operations Centre is built to close these gaps for organizations that cannot build that capability on their own.
The In-House SOC: What It Actually Requires
Building an in-house SOC is frequently presented as the premium option, the approach that gives an organization full control and maximum customization. The reality is more complex. The requirements for a functional in-house SOC are substantial, and the organizations that pursue this path often underestimate both the cost and the operational difficulty of sustaining it.
Staffing Requirements and Talent Scarcity
A 24/7 SOC requires enough analysts to cover all shifts without relying on individuals to work unsustainable hours. Industry guidance typically suggests a minimum of eight to ten analysts for genuine around-the-clock coverage, accounting for shift patterns, leave, sick time, and the turnover that is endemic to the security operations profession. Senior analysts and a SOC manager add to the headcount requirement.
This staffing requirement collides with a structural market reality: experienced SOC analysts are among the most sought-after professionals in the technology labor market. Recruiting and retaining qualified personnel requires competitive salaries, meaningful career development opportunities, and a work environment that does not burn analysts out through excessive alert volumes and inadequate tooling. Organizations that build SOCs without addressing these factors typically experience high turnover, persistent vacancies, and the coverage gaps that follow.
Technology and Platform Costs
A functional SOC requires a SIEM platform to collect and correlate log data, endpoint detection and response tools across the device fleet, network monitoring capabilities, threat intelligence feeds, and case management and orchestration platforms that coordinate analyst workflow. The licensing, implementation, and ongoing maintenance costs for this technology stack are significant. CyberSecOp's SIEM-as-a-service and managed detection and response capabilities reflect the investment required to build and maintain this infrastructure at an enterprise level.
The Alert Fatigue Problem
A fully deployed security monitoring stack generates an enormous volume of alerts, far more than an adequately staffed team can investigate with the depth each alert deserves. Alert fatigue, the desensitization that occurs when analysts must process thousands of low-quality alerts to find genuine threats, is a primary cause of missed detections and analyst burnout. Addressing it requires ongoing tuning of detection rules, suppression of known false positives, and the institutional knowledge about what normal looks like in a specific environment that takes months or years to develop.
The Knowledge Breadth Challenge
The threat landscape a SOC must monitor spans network-based attacks, endpoint compromises, cloud environment misconfigurations, identity-based intrusions, application vulnerabilities, and social engineering campaigns. No individual analyst has deep expertise across all of these domains. An in-house SOC of ten analysts is unlikely to have genuine specialists in all of them, which means some threat categories will be monitored by generalists rather than experts.
The Managed SOC: What It Delivers
A managed SOC provider operates a security operations function on behalf of multiple client organisations, providing 24/7 monitoring, threat detection, investigation, and response coordination as a service. CyberSecOp's managed SOC delivers this capability to organizations across industries, with detection and response tuned to the specific threat profiles of each client's environment.
Immediate Access to Established Expertise
A managed SOC provider has already built what an in-house SOC takes years to develop: an experienced analyst team, mature detection playbooks, tested incident response procedures, and a threat intelligence operation that tracks adversary activity across all client environments simultaneously. From the first day of engagement, the client organization benefits from this institutional maturity, without the years and investment required to build it internally.
Cross-Client Threat Intelligence
One of the structural advantages of the managed SOC model is the threat intelligence benefit of monitoring multiple organizations simultaneously. When a new attack technique is used against one client, the managed SOC provider identifies it, updates detection logic across all clients, and the benefit is shared immediately. An in-house SOC sees only what happens in one environment, a managed SOC provider sees what is happening across dozens or hundreds.
Technology Infrastructure at Scale
A managed SOC provider has already made the technology investments that an in-house SOC requires and amortizes those costs across its entire client base. The client organization gets access to enterprise-grade security technology, SIEM, EDR, network detection, threat intelligence, orchestration, and automation, without the capital expenditure, implementation project, or ongoing maintenance burden of owning it.
Scalability Without Hiring Cycles
Organizations grow, acquire businesses, expand into new geographies, and adopt new technology platforms. An in-house SOC must grow its headcount and technology footprint to keep pace, a process that involves hiring cycles measured in months. A managed SOC scales with the client's environment immediately, without the friction of internal procurement and hiring.
Side-by-Side Comparison
The following comparison covers the factors most relevant to the build-vs-buy decision. Costs are indicative ranges and will vary by organization size, industry, and market.
Annual cost (24/7 coverage): In-house: $1.5M–$3M+ including salaries, benefits, technology licensing, and infrastructure. Managed SOC: $80K–$400K annually depending on environment size and service tier.
Time to operational: In-house: 12–24 months from decision to functional 24/7 coverage. Managed SOC: 4–8 weeks from contract to active monitoring.
Analyst team depth: In-house: 8–12 analysts for genuine 24/7 coverage; expertise breadth limited by team size. Managed SOC: Full analyst team with specialists across network, endpoint, cloud, identity, and threat intelligence.
Technology stack: In-house: Separate procurement, implementation, and maintenance of SIEM, EDR, network monitoring, and orchestration platforms. Managed SOC: Enterprise-grade stack included; no capital expenditure or maintenance burden.
Threat intelligence: In-house: Limited to what the organization's own subscriptions and team provide. Managed SOC: Cross-client intelligence from monitoring multiple environments simultaneously.
Scalability: In-house: Requires hiring cycles and technology projects; lags behind growth. Managed SOC: Scales with the client environment on the existing contract.
Staff turnover risk: In-house: High; security analyst turnover averages 20–30% annually; departures create coverage gaps. Managed SOC: Managed by the provider; client continuity is unaffected by individual staffing changes.
Compliance reporting: In-house: Requires dedicated effort to produce audit-ready reporting. Managed SOC: Most providers include compliance-aligned reporting as part of the service.
When Does an In-House SOC Make Sense?
The in-house model is appropriate in a narrow set of circumstances. Very large enterprises with highly specialized security requirements, where the organization's threat profile is sufficiently unique that a managed provider cannot adequately tune detection, may justify the investment. Organizations with regulatory constraints that prohibit third-party access to security telemetry may have no alternative. And organizations that have already built a mature in-house SOC may find it more cost-effective to continue than to migrate.
For the vast majority of organizations, including SMBs and mid-market companies, the in-house SOC model is not a realistic path to the coverage it promises. The staffing costs are prohibitive, the talent market is hostile, and the technology investment is substantial. The organizations that pursue it anyway frequently end up with an under-resourced function that provides a false sense of security rather than genuine coverage.
The Hybrid Approach
Some organizations combine elements of both models, maintaining an internal security team for incident ownership, escalation, and organizational context while outsourcing the continuous monitoring function to a managed SOC provider. This approach gives internal teams the strategic and operational control they want while leveraging the managed provider's 24/7 coverage, tooling, and analyst depth. CyberSecOp's managed SOC services are designed to work collaboratively with internal security teams, functioning as an extension of the team rather than a replacement for it.
Making the Decision
The right choice depends on your organization's budget reality, talent market position, growth trajectory, regulatory environment, and risk tolerance. For most organizations, the honest assessment of what a genuine in-house SOC requires, and what it costs to sustain, leads to the same conclusion: the managed model delivers better coverage, at lower cost, with less operational risk.
CyberSecOp's managed SOC services provide 24/7 threat monitoring, investigation, and response coordination backed by a team of security specialists and enterprise-grade technology infrastructure. A cybersecurity assessment establishes the current security baseline and informs the scope and configuration of the managed service. Contact us at cybersecop.com/contact to discuss your requirements.
CyberSecOp Weekly Cybersecurity Digest October14 2026
The security developments that deserve attention this week — organized around active exploitation, vendor updates, emerging campaigns, and breach activity so security leaders can quickly prioritize action.
Weekly Cybersecurity Digest
The security developments that deserve attention this week — organized around active exploitation, vendor updates, emerging campaigns, and breach activity so security leaders can quickly prioritize action.
This Week’s Highest-Priority Threats
Four developments deserve immediate review because exploitation is active or was observed shortly after disclosure.
Auth Bypass / RCE Zero-Day
CVE-2026-104935 was added to CISA KEV after active exploitation. Attackers chained flaws to reach root and steal stored Active Directory credentials.
FortiBleed Campaign Remains Active
Attackers are using leaked and infostealer-sourced credentials against FortiGate devices, followed by credential capture and ransomware-linked activity.
October Patch Tuesday
October coverage counted 1,411 fixes, including an actively exploited Windows Shell Mark-of-the-Web security feature bypass and two publicly disclosed flaws.
Critical File-Read Flaw
CVE-2026-21589 affects eight Data Center products. Exploitation attempts were observed within roughly two hours of public technical details.
Important Vendor & Platform Updates
Not every issue is being exploited today, but several warrant accelerated remediation because of potential impact.
GitLab CE / EE
A maximum-severity unauthenticated RCE affects self-managed instances. Upgrade to fixed releases immediately.
SAP Cloud SDK for Python
OAuth2 SSRF could expose client credentials. Patch and restrict tenant_subdomain values where necessary.
Docker Hub
A fixed account-conversion flaw could allow registry actions as another user. Review recent image integrity and account changes.
Google Chrome
Three bugs were chained into a full exploit in research. Chrome 152 contains the fixes; relaunch browsers to apply them.
Ghostscript
A heap overflow can enable RCE through crafted PDFs in certain processing chains. Update to Ghostscript 10.08.0 or later.
curl / libcurl
An HTTP/2 upload use-after-free was fixed in curl 8.23.0. A PoC exists, though attacks were not reported in the digest.
Phishing, Mobile Malware & Identity Risk
This week also reinforced the importance of identity controls, user awareness, and application sourcing.
Hirudo Trojan
Hirudo uses fake apps and Accessibility permissions, then replaces legitimate banking apps with modified versions that disable protections.
Global Takedown
Law-enforcement action disrupted infrastructure tied to a network reported to have sent roughly one billion phishing messages.
Deployment Issue
Recent Windows updates may break Remote Desktop access for some non-admin users when Administrator protection is enabled.
End of Support
Home and Pro editions have reached end of support and no longer receive monthly security or preview updates.
Incidents That Show Where Exposure Becomes Impact
Three disclosed incidents highlight operational technology, retail disruption, and third-party concentration risk.
Supermarket Refrigeration Attack
Attackers reportedly hijacked older controllers and triggered overnight defrost cycles across hundreds of French supermarkets.
Business Systems Disrupted
A cyberattack disrupted IT systems supporting Hobbs, Whistles, and Phase Eight. Stores remained open while investigation continued.
Customer Data Exposure
Malware at a contractor exposed data tied to about 8.63 million customers and 93,000 employees of Daiichi Kosho.
What This Week Means for Your Program
VPNs, edge devices, collaboration platforms, and externally reachable infrastructure continue to attract rapid exploitation.
Phishing-resistant MFA, credential resets, session termination, and restricted admin exposure remain essential.
Security updates can introduce operational issues. Validate RDP and other critical workflows before enterprise deployment.
Contractors, cloud SDKs, registries, plugins, and embedded services can become indirect attack paths.
Operational systems can create immediate physical-world business impact when left internet-accessible.
The goal is not more alerts — it is faster decisions about what to patch, restrict, investigate, and retire.
Need help turning this week’s threats into business action?
CyberSecOp helps organizations assess exposure, prioritize vulnerabilities, strengthen monitoring, respond to incidents, and align security decisions with business risk.
Professional Services Cybersecurity: Why Consulting Firms, Accountants, and Advisors Are Prime Targets
Professional services firms are trusted with information that is valuable precisely because it belongs to someone else. Consulting firms hold strategic plans, contracts, credentials, acquisition data, product roadmaps, and sensitive internal communications.
Professional services firms are trusted with information that is valuable precisely because it belongs to someone else. Consulting firms hold strategic plans, contracts, credentials, acquisition data, product roadmaps, and sensitive internal communications. Accounting and tax practices hold Social Security numbers, financial records, tax returns, payroll information, and banking details. Legal and advisory firms handle confidential matters, transaction documents, regulated financial information, and communications that can influence high-value decisions. That concentration of client data makes professional services cyber security a business-critical requirement, not simply an information technology concern.
Attackers also understand how these firms work. Professional services businesses depend heavily on email, cloud collaboration, remote access, document sharing, and constant communication with clients and third parties. Trust is part of the delivery model, so a compromised mailbox, stolen credential, fraudulent payment instruction, or exposed document repository can be used against both the firm and its clients. CyberSecOp’s Managed Security Services address this risk by combining monitoring, threat detection, identity and network protection, incident response, compliance support, and security governance instead of treating each threat as a separate problem.
Why Professional Services Firms Are Attractive Cyber Targets
The Data Is High Value and Highly Portable
Professional services firms may not operate factories or large consumer platforms, but they often possess concentrated collections of sensitive information. A single accounting practice can hold years of tax records and identity data. A consulting firm may have confidential strategy materials from dozens of clients. A law firm can hold litigation records, deal documents, intellectual property, and privileged communications. Much of this information is stored in email, cloud drives, practice management systems, customer relationship management platforms, and collaboration tools, which makes stolen credentials especially useful to an attacker.
The 2026 Verizon Data Breach Investigations Report found that vulnerability exploitation had become the leading initial breach entry point across its dataset, at 31 percent, and that third-party involvement had risen sharply to 48 percent of breaches. Those findings matter to professional services because these firms frequently rely on software-as-a-service platforms, outsourced information technology, payroll providers, document portals, cloud storage, and client-connected systems. A mature Third-Party Risk Management program therefore has to evaluate both the security of the firm and the security dependencies around it.
Email Is Both a Business Tool and an Attack Surface
Few industries rely on email more heavily than professional services. Engagement letters, invoices, payment instructions, document requests, executive approvals, client questions, and urgent changes all arrive through the same channel. This makes Business Email Compromise (BEC) particularly dangerous because the attacker does not need to deploy malware if a believable message can persuade an employee or client to act.
The Federal Bureau of Investigation’s Internet Crime Complaint Center reported roughly $3 billion in Business Email Compromise losses during 2025. The fraud is effective because it exploits context and trust. Attackers may impersonate a partner, compromise a real client account, change payment details in an active invoice thread, or use information gathered from previous messages to make a request appear routine. Technical controls can reduce the opportunity, but strong defense also requires monitoring, identity protection, payment verification procedures, and Security Awareness Training built around the workflows employees actually use.
A Compromised Firm Can Become a Route Into Its Clients
Professional services firms are often connected to their clients through shared platforms, privileged accounts, remote administration, file exchange, project tools, or trusted email relationships. That creates an amplification effect. An attacker who compromises one firm may gain access to several client environments or use the firm’s identity to deliver convincing social engineering attacks. This is one reason the security posture of a consulting, accounting, or advisory provider increasingly appears in customer due diligence and vendor security reviews.
The Regulatory and Professional Obligations Are Getting Stronger
Accounting and Tax Practices
For tax and accounting professionals, cybersecurity is tied directly to federal safeguarding requirements. In August 2026, the Internal Revenue Service and Security Summit partners again reminded tax professionals that federal law requires tax and accounting professionals to create and maintain a Written Information Security Plan (WISP) to protect client information. The plan is expected to address employee management, information systems, risk assessment, safeguards, monitoring, service providers, and ongoing adjustment as circumstances change.
A written plan alone is not enough if controls are not operating. CyberSecOp’s Regulatory IT Compliance Consulting can help translate legal and framework requirements into policies, technical safeguards, testing, documentation, and ongoing evidence. For firms that do not have a dedicated security executive, Virtual Chief Information Security Officer (vCISO) services can provide ownership and executive oversight for the security program rather than leaving compliance scattered across information technology, operations, and outside vendors.
Investment Advisers and Financial Advisory Firms
Financial advisory firms may also fall under specific Securities and Exchange Commission (SEC) requirements. Amendments to Regulation S-P require covered institutions, including registered investment advisers, to maintain written incident response policies and procedures for unauthorized access to or use of customer information and, in many circumstances, to notify affected individuals no later than 30 days after becoming aware of a qualifying incident. Larger entities had a December 3, 2025 compliance date, and smaller entities had a June 3, 2026 compliance date. By September 2026, both compliance dates have passed.
These requirements make incident detection and investigation operational compliance capabilities. A firm cannot reliably meet a notification obligation if it does not know when an incident occurred, what information was affected, or whether unauthorized use is reasonably likely. Continuous monitoring through a Security Operations Center, combined with an established Incident Response Services relationship, can help reduce the time between suspicious activity, investigation, containment, and regulatory decision-making.
Law Firms and Client Confidentiality
Law firms face a different but equally serious responsibility. American Bar Association Model Rule 1.6(c) states that lawyers should make reasonable efforts to prevent inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to client representation. The exact legal and ethical obligations vary by jurisdiction and matter, but the security principle is clear: confidentiality depends on reasonable safeguards, not just professional discretion. CyberSecOp’s Law Firm Security Consulting is designed around the combination of client confidentiality, business risk, security controls, and regulatory expectations that legal practices have to manage.
The Threat Profile of Professional Services
Credential Theft and Account Takeover
Cloud email and collaboration systems are central to professional services, so credentials are high-value targets. A stolen password may expose years of correspondence, shared documents, client contacts, calendars, and active transaction details. Attackers can then create mailbox rules, monitor conversations, impersonate the account owner, or use the account to reset access elsewhere. Multifactor authentication, conditional access, identity monitoring, endpoint security, and rapid investigation of suspicious sign-ins should be treated as baseline controls.
Ransomware and Data Extortion
Ransomware is especially disruptive for service firms because revenue depends on continuous access to documents, communications, project systems, and client files. Modern ransomware attacks may also involve data theft before encryption, creating confidentiality and notification problems even when backups restore operations. Defense requires more than backup software. It requires secure identity, patching, endpoint detection, network segmentation, recovery testing, and response procedures that have been exercised before an incident.
Payment and Invoice Fraud
Accounting departments and client service teams routinely process invoices, retainers, settlement instructions, vendor payments, payroll changes, and expense requests. Attackers exploit normal urgency by requesting a bank change, new wire destination, or confidential tax document. Firms should separate the communication channel that requests a financial change from the channel that verifies it. High-risk payment changes should be confirmed using known contact information rather than the phone number or link included in the requesting message.
Third-Party and Cloud Risk
The technology stack of a professional services firm is often mostly external. Email, document management, customer relationship management, tax software, e-signature, payroll, billing, conferencing, and backup may all be delivered by vendors. This can improve reliability and security, but it also changes the attack surface. Vendor access, shared responsibility, authentication controls, data residency, breach notification terms, and offboarding procedures must be understood before sensitive client information is entrusted to a platform.
Why Basic IT Support Is Not Enough
Managed information technology services and cybersecurity services overlap, but they are not interchangeable. Information technology support is generally optimized for availability, user productivity, device management, and troubleshooting. Security requires adversarial thinking, continuous detection, threat intelligence, risk assessment, forensic readiness, compliance mapping, and the ability to respond when normal operations are being deliberately manipulated by an attacker. A help desk that can reset a password is useful, but it is not the same as a team that can determine whether the account was compromised, identify what the attacker accessed, contain persistence, and preserve evidence.
CyberSecOp’s Managed Detection and Response services and managed security capabilities are designed to supplement internal and outsourced information technology teams with dedicated security functions. That separation of responsibility is especially important for professional services firms where the same systems that employees use for routine work also contain the firm’s most sensitive client information.
How CyberSecOp Managed Services Address Professional Services Risk
Start With a Risk and Security Assessment
The first step is understanding what the firm actually needs to protect. CyberSecOp’s Cybersecurity Assessment Services evaluate technology, security controls, policies, employee practices, and business processes to identify gaps that create meaningful exposure. For professional services, the assessment should map high-value client data, privileged accounts, external sharing, vendor access, remote work, payment workflows, and regulatory requirements before selecting additional tools.
Monitor Identity, Endpoints, Networks, and Cloud Activity
Continuous monitoring provides the visibility needed to identify abnormal behavior early. Managed security can correlate suspicious login activity, endpoint alerts, network events, cloud access, and other telemetry so that a sequence of weak signals is not treated as unrelated noise. This is particularly important for account takeover, where the attacker may use valid credentials and legitimate applications rather than obvious malware.
Build Security Around Compliance, Not Beside It
Professional services firms often experience compliance as questionnaires, audits, insurance applications, and client requirements. A stronger model treats these demands as evidence of an underlying security program. Governance, access control, incident response, vendor management, training, testing, and documentation should reinforce one another. The vCISO can coordinate priorities and executive reporting, while compliance specialists map controls to the obligations that actually apply to the firm.
Prepare for the Incident Before It Happens
An incident response plan should identify decision-makers, escalation paths, legal counsel, cyber insurance requirements, forensic contacts, communication procedures, recovery priorities, and regulatory notification responsibilities. Tabletop exercises can expose unclear authority or missing information before a real incident forces the organization to make those decisions under pressure. For a firm built on client trust, the quality of the response can be as important as the initial technical containment.
A Practical Security Baseline for Professional Services Firms
At minimum, professional services organizations should know where sensitive client information is stored, require strong multifactor authentication, maintain managed endpoint protection, patch internet-facing systems promptly, restrict administrative access, encrypt sensitive data, control external sharing, back up critical systems, test recovery, train employees against phishing and payment fraud, review high-risk vendors, monitor security events, and maintain an incident response plan. The controls should be scaled to the size and risk of the business, but none should exist only on paper.
Protect the Trust Your Business Is Built On
Professional services firms sell expertise, judgment, confidentiality, and trust. A cyber incident can damage all four at once. The threat is not limited to large multinational firms. Attackers can monetize the client data, credentials, payment workflows, and trusted relationships of a small advisory practice just as effectively, and smaller firms often have fewer dedicated resources to detect the compromise.
For firms comparing cyber security professional services, the benchmark should be whether one provider can connect strategic oversight, regulatory requirements, technical monitoring, and incident response without creating more fragmented responsibility. CyberSecOp combines Professional Services Security Consulting, managed security, compliance support, vCISO leadership, security assessments, and incident response to help firms build a program that reflects how they actually operate. If your consulting, accounting, legal, or advisory business is relying on general information technology support to carry the full cybersecurity burden, contact CyberSecOp to evaluate the gaps and build a security model that protects both your firm and the clients who trust it.
IT Security Consulting Services: What to Look For and What to Avoid
Choosing IT security consulting services is difficult because almost every provider can present the same high-level promises: reduce risk, improve compliance, secure the cloud, stop threats, and strengthen resilience.
Choosing IT security consulting services is difficult because almost every provider can present the same high-level promises: reduce risk, improve compliance, secure the cloud, stop threats, and strengthen resilience. The meaningful differences appear after the sales presentation, in how the consulting firm defines scope, validates risk, assigns experienced people, communicates findings, supports remediation, and responds when something goes wrong. A strong IT security consulting partner should leave the organization with better decisions and stronger operating capability, not just another report.
Buyers should evaluate security consulting the same way they evaluate other high-consequence professional services. Credentials matter, but only when they match the work. Service Level Agreements (SLAs) matter, but only when the escalation process behind them is real. A broad service catalog can be valuable, but only when specialists are available to execute each discipline. CyberSecOp’s consulting model spans assessments, compliance, incident response, managed security, network security, penetration testing, and Virtual Chief Information Security Officer (vCISO) support, which provides a useful benchmark for what a full-service security consulting relationship can look like.
Start With the Problem You Need the Consultant to Solve
The first mistake buyers make is shopping for a provider before defining the business problem. “Improve cybersecurity” is not a usable scope. A better starting point is a concrete outcome: prepare for a compliance assessment, reduce ransomware exposure, build an incident response program, redesign network security, validate cloud controls, conduct penetration testing, establish a governance program, or provide ongoing security leadership. The right provider should help refine the scope, but it should not convert every problem into the product or service it happens to sell most aggressively.
A structured Cybersecurity Assessment is often the best starting point when the organization does not yet know where its highest risks are. A good assessment should connect technical findings to business impact, distinguish urgent weaknesses from lower-priority improvements, and produce a realistic remediation roadmap. If the engagement begins with recommendations before the consultant has understood the environment, the provider is solving from a template rather than from evidence.
Look for Relevant Experience, Not a Wall of Logos
Certifications Should Match the Engagement
Professional certifications can demonstrate a baseline of knowledge and experience, but no single credential proves that a consultant is right for every task. Certified Information Systems Security Professional (CISSP) certification, for example, requires candidates to meet multi-year experience requirements across security domains. Certified Information Security Manager (CISM) certification similarly emphasizes professional experience in security management. These credentials can be meaningful for governance, architecture, risk, and program leadership, but they do not automatically establish expertise in malware forensics, cloud engineering, industrial control systems, or penetration testing.
Ask which individuals will actually perform the work and which qualifications they hold that are relevant to that work. Compliance engagements may require expertise in the specific framework or regulation. Offensive testing should be performed by practitioners with demonstrable penetration testing experience. Incident response should involve investigators who routinely handle live incidents. Cloud reviews should include engineers with direct experience in the platforms being assessed. The evaluation should focus on the delivery team, not only the credentials of company leadership.
Industry Experience Matters When the Risk Context Changes
A strong consultant understands that the same technical weakness can have different consequences in healthcare, financial services, legal services, manufacturing, government contracting, or education. Regulatory obligations, data sensitivity, operational downtime, third-party dependencies, and tolerance for system changes vary significantly. Ask for examples of similar environments and, where confidentiality permits, the types of problems the team has solved. The goal is not to buy a generic “industry package.” It is to verify that the consultant understands the business consequences behind the controls.
Evaluate the Scope of Services Before You Evaluate the Price
Security consulting can range from a narrow project to an ongoing operating relationship. A provider that performs excellent penetration testing may not be the right firm to build a governance program. A compliance specialist may not be able to provide 24/7 incident response. A managed monitoring company may be strong at alert triage but weak at board-level risk strategy. Buyers should determine whether they need a specialist or a provider that can coordinate multiple disciplines.
CyberSecOp’s Cyber Security Consulting Services include advisory work, cybersecurity assessments, incident response, penetration testing, privacy and compliance services, compromise assessment, and related managed services. A broad capability set matters when findings in one area create work in another. For example, a risk assessment may identify weak segmentation, which requires Network Security Services; a compliance review may expose missing incident procedures, which requires Incident Response Services; or executive governance gaps may point to Virtual Chief Information Security Officer (vCISO) services.
Demand a Clear Methodology and Deliverables
The Scope Should State What Is In and Out
Before work begins, the statement of work should identify systems, locations, business units, applications, cloud environments, frameworks, testing methods, assumptions, dependencies, and exclusions. If the consultant is performing technical testing, the rules of engagement should define when testing occurs, what techniques are permitted, who can authorize changes, and how critical findings are escalated. Ambiguity at this stage creates disputes later because the customer expects a comprehensive review while the provider believes it sold a limited sample.
Findings Should Be Prioritized by Risk
A useful security report does more than list vulnerabilities. It explains the condition, evidence, likelihood, business impact, affected assets, recommended remediation, and priority. Automated scanner output can be part of the evidence, but it should not be the finished consulting deliverable. Consultants add value by validating what matters and helping decision-makers understand what should be fixed first.
Remediation Support Should Be Defined Up Front
Many projects fail in the gap between finding a problem and fixing it. Ask whether remediation guidance is included, whether the consultant will review proposed fixes, whether retesting is part of the scope, and whether the team can help implement changes when needed. A consulting firm does not have to perform every remediation task, but responsibility should be explicit. Otherwise, the engagement can end with a long list of risks and no practical path to reduce them.
Examine Service Level Agreements Closely
A Service Level Agreement should define measurable expectations for the services where time matters. For an assessment project, this may include communication and deliverable timelines. For managed services and incident response, the agreement should distinguish severity levels, notification targets, escalation procedures, availability, customer responsibilities, and what constitutes acknowledgement versus active investigation. There is no universal response-time number that is appropriate for every organization, so a provider that offers one generic promise without discussing severity and business impact is oversimplifying the problem.
The National Institute of Standards and Technology (NIST) updated Special Publication 800-61 Revision 3 in 2025 to integrate incident response into broader cybersecurity risk management. The guidance emphasizes preparation, defined roles, coordination, detection, response, and recovery. This is a useful lens for evaluating a consulting partner: during a serious incident, who has authority, who investigates, who communicates with leadership, how external specialists are engaged, and how recovery is coordinated? CyberSecOp’s Incident Response Services and 24/7 support model are designed to provide a defined path when response becomes urgent.
Ask How the Consultant Handles Security and Confidentiality
Security consultants may receive privileged access to systems, vulnerability details, network diagrams, employee information, regulatory evidence, credentials, logs, and incident data. The provider therefore becomes part of your risk environment. Ask how access is approved and removed, how customer data is stored, whether multifactor authentication is required, how workstations are secured, how sensitive findings are transmitted, how long evidence is retained, and whether subcontractors are used.
Third-party oversight should also extend to the consultant’s own suppliers. If the provider uses external scanning platforms, cloud storage, ticketing systems, forensic tools, or subcontracted specialists, the customer should understand where sensitive information goes and which contractual safeguards apply. CyberSecOp’s Managed Vendor Risk Management approach reflects the same principle organizations should apply when evaluating any security partner: trust should be supported by evidence, defined controls, and ongoing oversight.
Look for the Ability to Connect Strategy and Operations
A common weakness in consulting engagements is the separation of strategy from execution. One team creates a three-year roadmap, another provider monitors alerts, a third runs annual penetration tests, and no one owns the overall security outcome. The National Institute of Standards and Technology Cybersecurity Framework 2.0 added greater emphasis on governance because cybersecurity risk has to be managed alongside other enterprise risks. A consulting partner should be able to explain how policies, architecture, monitoring, vulnerability management, compliance, response, and executive reporting connect.
This is where a vCISO model can be particularly valuable for mid-sized organizations. The vCISO provides ongoing leadership and prioritization while specialist teams execute technical work. Instead of receiving independent recommendations from multiple vendors, the organization has a security roadmap and an accountable leadership function that can track remediation, report progress, and adjust priorities as the environment changes.
Red Flags to Avoid When Hiring IT Security Consulting Services
Guaranteed Compliance or Guaranteed Security
No responsible consultant can guarantee that an organization will never be breached, and compliance outcomes depend on scope, implementation, evidence, auditor interpretation, and ongoing operations. Be cautious of firms that promise certification or compliance before assessing the environment. A credible provider can help prepare, implement controls, test readiness, and reduce risk, but it should be precise about what it controls and what the customer must do.
Tool-First Recommendations
If every discovery conversation quickly turns into a product demonstration, the consulting process may be a sales channel for software. Technology is necessary, but controls should be selected because they address a defined risk and fit the organization’s architecture, staff, and budget. The correct sequence is understand the environment, identify risk, define required outcomes, then choose technology.
Vague Staffing and Heavy Subcontracting
Ask who will lead the engagement, who will perform the technical work, whether those people are employees or subcontractors, and whether substitutions require approval. Senior experts who appear during the sales process should not disappear once the contract is signed unless the delivery model was explained from the beginning. Subcontracting is not inherently a problem, but hidden subcontracting is.
Reports Without Evidence or Prioritization
A 150-page report is not automatically a better deliverable than a 30-page report. Watch for findings that are copied directly from tools, lack evidence, do not identify affected systems, or assign every issue the same urgency. The best deliverable is one that enables action. Executives should understand the business priorities, technical teams should understand what to change, and the organization should be able to verify that remediation occurred.
No Clear Incident Escalation Path
If a consultant discovers active compromise during an assessment, or if a managed service detects a critical threat at night, the organization should already know what happens next. Ask for the escalation path in writing. Determine whether the provider can move from advisory work into investigation and containment, or whether you will need to find another company during the incident. A pre-established response relationship reduces confusion when time is limited.
How to Compare Security Consulting Proposals
Compare providers across the same categories: business understanding, scope, delivery team, relevant experience, methodology, access to specialists, deliverables, remediation support, response capability, security controls, reporting, service levels, references, exclusions, and total cost. Do not compare only hourly rates. A lower-priced engagement that produces unvalidated findings or excludes remediation can become more expensive once the organization has to repeat the work with another provider.
Also distinguish project cost from long-term operating cost. A one-time assessment may identify a gap, but the organization may still need monitoring, governance, compliance maintenance, or managed security afterward. CyberSecOp’s Managed Security Services can extend project findings into continuous operations, while Security Awareness Training, penetration testing, compliance consulting, and vCISO services can be incorporated as the security program matures.
Why CyberSecOp Is a Strong Benchmark for IT Security Consulting
A capable consulting partner should be able to move from understanding risk to implementing and operating the controls needed to reduce it. CyberSecOp provides cybersecurity consulting, risk and security assessments, Regulatory IT Compliance Consulting, network security, penetration testing, managed security, managed detection and response, incident response, and vCISO services. That breadth allows an organization to keep strategic guidance and operational execution connected while still selecting only the services it actually needs.
The right IT security consulting relationship should create clarity: which risks matter, which controls are required, who owns each action, how quickly issues are escalated, how progress is measured, and what the organization should do next. If you are evaluating security consulting firms or replacing a provider that has not delivered that level of accountability, contact CyberSecOp to discuss your environment, define the right scope, and build a security roadmap that can move from assessment to measurable risk reduction.
What Is Cybersecurity as a Service (CSaaS) and Is It Right for Your Business?
Cybersecurity as a Service (CSaaS) is an outsourced security model that gives an organization ongoing access to cybersecurity people, processes, technology, and program oversight through a recurring service relationship.
Cybersecurity as a Service (CSaaS) is an outsourced security model that gives an organization ongoing access to cybersecurity people, processes, technology, and program oversight through a recurring service relationship. Instead of assembling every capability internally, a business uses a specialist provider to deliver and coordinate functions such as threat monitoring, security assessments, compliance support, vulnerability management, incident response readiness, and security leadership. CyberSecOp Cyber Security as a Service (CSaaS) is designed around that broader model, with coverage that can extend across cloud, hybrid, and on-premises environments.
The appeal of the model is not simply outsourcing. It is consolidation and continuity. Many organizations already buy security products, periodic penetration tests, cyber insurance, compliance consulting, and a basic managed security retainer from different vendors. The result can still be a fragmented program with unclear ownership. CSaaS brings those activities into a coordinated operating model that can be scaled to the organization’s risk, regulatory obligations, technology environment, and internal staffing. The central question is therefore not whether outsourced security is useful. It is whether your business needs a complete security capability, a narrower Managed Security Services Provider (MSSP) relationship, or a larger in-house team.
What Cybersecurity as a Service Actually Means
The term Cybersecurity as a Service is used broadly in the market, so buyers should look past the label and examine the operating model. A mature CSaaS engagement should not be limited to a single security tool or a dashboard that produces alerts. It should combine security expertise with repeatable processes and technology operations so that risks are identified, prioritized, addressed, and reported over time. In practical terms, the provider becomes an extension of the organization’s information technology and risk functions rather than an outside vendor that appears only when a project is scheduled.
A useful way to evaluate the model is through the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) 2.0. NIST organizes cybersecurity outcomes across six functions: Govern, Identify, Protect, Detect, Respond, and Recover. CSaaS can support all six when it combines governance, assessment, protective controls, continuous monitoring, incident response, and recovery planning. This is broader than simply watching logs or managing a firewall. CyberSecOp’s Cybersecurity Assessment Services can establish the current-state risk baseline, while ongoing managed services and advisory support turn the assessment into a continuously operated program.
What a CSaaS Program Can Include
Security Governance and Program Leadership
Cybersecurity decisions are business decisions. Someone must determine risk tolerance, approve priorities, assign responsibility, report to leadership, and keep security aligned with regulatory and contractual obligations. Organizations without a full-time security executive can incorporate Virtual Chief Information Security Officer (vCISO) services into a CSaaS model. This gives management access to experienced security leadership without requiring every strategic responsibility to sit with the Chief Information Officer, information technology manager, or operations team.
Continuous Monitoring, Detection, and Response
The operational core of many CSaaS programs is continuous security monitoring. A Security Operations Center (SOC) as a Service can collect and analyze telemetry from endpoints, identities, networks, cloud services, and security tools. Managed Detection and Response (MDR) adds investigation and response capability so that high-priority activity is not merely placed into a queue. The distinction matters because detection without a defined path to investigation, containment, and escalation leaves the customer carrying much of the operational burden.
Vulnerability and Exposure Management
Periodic vulnerability scans provide a snapshot. A service model can make vulnerability and exposure management continuous by tracking new assets, newly disclosed weaknesses, configuration problems, remediation status, and changes in external attack surface. Testing can also be deepened with penetration testing services when the organization needs to validate whether identified weaknesses can actually be exploited and how far an attacker could move after initial access.
Compliance and Security Program Support
Security and compliance overlap, but they are not identical. A CSaaS engagement can help map controls to applicable frameworks, maintain evidence, update policies, prepare for assessments, and identify gaps created by business or technology changes. CyberSecOp’s Regulatory IT Compliance Consulting supports requirements across frameworks and regulated environments, while the broader service model keeps required controls operating after the initial readiness project is complete.
Incident Response Readiness
An organization can have strong preventive controls and still experience an incident. A complete CSaaS model should therefore define how incidents are declared, who has authority to act, how evidence is preserved, how legal and executive stakeholders are engaged, and how recovery decisions are made. CyberSecOp’s Incident Response Services can be integrated with ongoing monitoring so that the organization does not begin searching for qualified responders after a breach is already underway.
CSaaS vs. an In-House Security Team
An in-house security function provides direct control and deep organizational context, which can be valuable for large enterprises, highly specialized environments, and organizations with enough scale to support dedicated teams. The challenge is that a functioning program requires more than one generalist. Security architecture, compliance, monitoring, engineering, identity, cloud security, vulnerability management, threat analysis, and incident response are different disciplines. Coverage also has to continue during vacations, turnover, nights, weekends, and major incidents.
The labor economics are significant. The U.S. Bureau of Labor Statistics reported a median annual wage of $129,180 for information security analysts in May 2025. That figure represents one role before benefits, recruiting costs, training, management overhead, security tooling, and the additional specialists needed to create resilient 24-hour coverage. For many small and mid-sized organizations, the real comparison is therefore not CSaaS versus the salary of one employee. It is CSaaS versus the combined cost of a multi-role security capability and the technology required to operate it.
CSaaS does not eliminate the need for internal ownership. Business leaders still own risk, approve priorities, and make decisions that affect operations. The model works best when responsibility is explicit: the provider supplies specialized capability and continuous execution, while the customer retains governance authority and business context.
CSaaS vs. a Basic MSSP Retainer
A traditional Managed Security Services Provider relationship often focuses on a defined operational scope, such as managed firewalls, endpoint monitoring, Security Information and Event Management (SIEM), alert triage, or Managed Detection and Response. Those services can be highly valuable, but they do not automatically create a complete security program. The customer may still need separate resources for policies, compliance, risk assessment, executive reporting, third-party risk, employee training, architecture, and incident planning.
CSaaS is broader when it intentionally combines those functions under one operating model. For example, a monitoring team may detect suspicious access, while the governance team determines whether the event creates a regulatory obligation, the incident response team investigates and contains it, and the vCISO updates leadership on business impact. When these capabilities are purchased separately, the customer has to coordinate the handoffs. When they are designed as one service, the handoffs can be built into the program.
How the Cost Structures Differ
In-House Security Cost Structure
The in-house model is dominated by fixed and semi-fixed costs. Salaries, benefits, recruiting, retention, training, software licensing, logging infrastructure, endpoint protection, vulnerability tooling, and after-hours coverage must be funded regardless of whether the organization experiences a major incident that month. The advantage is dedicated internal capacity. The disadvantage is that adding a new capability generally means hiring, training, or purchasing another tool.
Basic Managed Security Retainer Cost Structure
A basic MSSP retainer is usually narrower and therefore easier to price. Cost commonly scales with endpoints, users, log volume, devices, cloud resources, or a defined service tier. This can be efficient when the organization already has internal security leadership and only needs specific operational functions outsourced. It becomes less efficient when the company repeatedly adds separate projects for compliance, assessments, executive advisory, incident response, and other uncovered responsibilities.
CSaaS Cost Structure
Cybersecurity as a Service typically shifts more of the security program into a recurring operating expense. The actual price depends on scope, environment size, coverage hours, regulatory complexity, technologies managed, response obligations, and the level of strategic support required. The economic value comes from shared specialist capacity. Instead of hiring a full-time expert for every discipline, the organization pays for access to the right expertise and operational capability as part of the service. A well-designed contract should clearly identify what is included, what triggers additional charges, which tools are part of the service, and what remains the customer’s responsibility.
When CSaaS Delivers the Most Value
Your Business Has Outgrown Informal Security
CSaaS is a strong fit when security has become too important to be handled as an additional responsibility for a systems administrator or information technology manager, but the business is not ready to build a full internal security department. Growth often exposes gaps in identity management, vendor oversight, policy governance, cloud configuration, and incident response that were manageable when the company was smaller.
You Face Multiple Compliance or Customer Requirements
Organizations that answer security questionnaires, undergo audits, pursue certifications, or handle regulated data need evidence that controls are not only documented but operating. A recurring service can connect compliance work to real technical operations. Third-Party Risk Management can also be incorporated when customers, suppliers, software providers, and cloud services expand the organization’s exposure beyond its own network.
You Need 24/7 Capability Without 24/7 Internal Staffing
Cyber incidents do not follow business hours. Companies that cannot justify a staffed internal Security Operations Center can use a managed model for continuous monitoring and escalation while keeping internal decision-makers on defined call paths. This is particularly valuable for ransomware, account takeover, suspicious cloud access, and other events where hours of delay can materially increase impact.
Your Security Tools Are Fragmented
Buying more technology does not automatically improve security. Organizations often accumulate overlapping products that are poorly integrated, inconsistently configured, or not actively monitored. CSaaS can rationalize the environment by deciding which controls are actually needed, integrating telemetry, assigning owners, and connecting technical findings to remediation. Managed Network Security Services and employee Security Awareness Training can then operate as parts of the same risk program rather than isolated initiatives.
When CSaaS May Not Be the Right Model
CSaaS is not automatically the best choice for every organization. A large enterprise with mature security leadership, specialized engineering teams, a fully staffed Security Operations Center, and established compliance functions may need only targeted external expertise. At the other end of the spectrum, a very small organization with limited technology and low regulatory exposure may be better served by a narrower managed service combined with a periodic assessment. The correct model depends on risk, complexity, internal capability, and how much of the security lifecycle the organization genuinely needs a provider to operate.
Questions to Ask Before Choosing a CSaaS Provider
Before signing a Cybersecurity as a Service agreement, ask who owns each security function, what monitoring is continuous, how incidents are escalated, what response assistance is included, which technologies are supported, how compliance work is handled, how often leadership receives reporting, how third parties are assessed, and how the service changes as the organization grows. The provider should be able to explain the complete operating model in plain language. If the answer is primarily a list of products, the offering may be a tool bundle rather than a true service.
Is Cybersecurity as a Service Right for Your Business?
The strongest candidates for CSaaS are organizations that need enterprise-level security outcomes without building every capability internally. They may have a capable information technology team but lack dedicated security leadership, 24/7 monitoring, compliance depth, or incident response expertise. They may also be growing quickly, entering regulated markets, responding to customer security requirements, or trying to replace a collection of disconnected vendors with a more accountable operating model.
CyberSecOp’s Cyber Security as a Service approach combines cybersecurity expertise with ongoing protection, compliance support, threat monitoring, and security operations across cloud, hybrid, and on-premises environments. If you are deciding between expanding an internal team, adding a basic MSSP retainer, or moving to a broader CSaaS model, start by measuring the capabilities you have today against the risks the business actually needs to manage. Contact CyberSecOp to discuss the right service structure for your environment and build a security program that can scale with the business.
Data Privacy Laws in 2026: How MSSPs Help Businesses Stay Compliant
The global data privacy landscape has changed more in the past five years than it did in the preceding two decades. What began with the General Data Protection Regulation establishing a comprehensive framework for personal data rights in Europe has expanded into a worldwide proliferation of privacy legislation, state by state, country by country, that now affects virtually every business that collects, processes, or transfers personal information. In 2026, that regulatory momentum has not slowed. It has accelerated.
Organizations that managed GDPR compliance as a one-time project have discovered that privacy compliance is an ongoing operational discipline, not a certification to be achieved and filed away. New regulations continue to emerge, existing frameworks are being revised and strengthened, enforcement is intensifying, and the technical and organizational requirements imposed by privacy law are becoming more demanding, not less. For most businesses, maintaining compliance across this evolving landscape requires the kind of continuous program management that a Managed Security Services Provider (MSSP) with dedicated compliance expertise is structured to provide.
The Regulatory Landscape in 2026
GDPR Enforcement Comes of Age
The European Union's General Data Protection Regulation has been in force since 2018, but the early years of enforcement were characterized by regulatory bodies building capacity, establishing precedent, and working through a backlog of complaints. That period is over. European data protection authorities have issued increasingly substantial fines across a wide range of violation categories: inadequate data security, unlawful data transfers, insufficient legal basis for processing, and failure to honor data subject rights;and the enforcement trend is toward greater frequency and higher penalties, not less.
The EU has also continued to develop and refine the broader digital regulatory framework surrounding GDPR. The Digital Services Act, the Digital Markets Act, and the EU AI Act each carry data protection implications that intersect with GDPR obligations,creating a layered compliance environment that requires coordinated attention across multiple regulatory instruments simultaneously.
US State Privacy Laws: A Patchwork Becomes a Pattern
The United States federal government has not enacted comprehensive privacy legislation, but the absence of a federal standard has not meant an absence of regulation. By 2026, more than twenty states have enacted their own comprehensive data privacy laws, most modeled in some variation on the California Consumer Privacy Act and its successor, the California Privacy Rights Act. Virginia, Colorado, Connecticut, Texas, Florida, Oregon, Montana, and a growing list of additional states have all enacted privacy frameworks that impose data subject rights, consent requirements, data minimization obligations, and security requirements on businesses that serve their residents.
The practical challenge for multi-state businesses is that these laws, while similar in structure, differ in scope, thresholds, exemptions, and specific requirements in ways that require individual analysis. A compliance program built around California's framework will not automatically satisfy Texas's requirements, and businesses operating nationally must maintain awareness of the specific obligations that apply in each state where they have a meaningful number of consumers.
Sector-Specific Regulatory Developments
Beyond general privacy legislation, sector-specific regulations have continued to evolve in ways that significantly affect cybersecurity and compliance programs. The SEC's cybersecurity disclosure rules require public companies to report material cybersecurity incidents within four business days and to disclose their cybersecurity risk management processes in annual filings. The FTC has expanded its enforcement of data security requirements under Section 5 of the FTC Act, with a particular focus on businesses that fail to implement reasonable security measures for personal data. Healthcare regulators have proposed updates to the HIPAA Security Rule that would impose more prescriptive technical requirements on covered entities and business associates. Financial services regulators, including the OCC, FDIC, and Federal Reserve, have implemented interagency guidance on cybersecurity risk management that applies to the banking sector. CyberSecOp's Compliance Security Consulting team maintains current expertise across all of these regulatory developments, translating regulatory language into actionable security and compliance requirements.
International Privacy Frameworks Beyond GDPR
GDPR has served as a model for privacy legislation around the world, and the countries that have enacted GDPR-influenced frameworks now represent a significant portion of the global economy. Brazil's Lei Geral de Proteção de Dados, Canada's evolving privacy framework, India's Digital Personal Data Protection Act, and privacy legislation across Southeast Asia, the Middle East, and Latin America all create compliance obligations for businesses with international operations or customer bases. Transfers of personal data between jurisdictions,always a complex area under GDPR,have become more complex as additional countries establish their own adequacy requirements and transfer mechanism frameworks.
The Key Compliance Requirements Businesses Must Address
Data Mapping and Processing Records
Most comprehensive privacy regulations require organizations to maintain detailed records of their data processing activities,what personal data they collect, from whom, for what purposes, how long it is retained, with whom it is shared, and where it is stored or transferred. This requirement, straightforward in principle, is enormously complex in practice for organizations with large, distributed technology environments and multiple third-party data relationships. Data mapping is not a one-time exercise, it must be maintained as a living record that reflects changes in systems, vendors, and business processes.
Data Subject Rights Management
Privacy regulations consistently grant individuals rights over their personal data, the right to access it, correct it, delete it, restrict its processing, receive it in portable form, and object to certain uses. Satisfying these rights within the timelines specified by applicable law requires operational processes and technical capabilities that many organizations have not fully built out. A data subject access request that spans data held in twenty different systems, managed by six different vendors, and subject to three different retention schedules requires a coordinated response infrastructure that does not emerge from a spreadsheet.
Consent and Legal Basis Management
Privacy regulations generally require that personal data processing be grounded in a lawful legal basis, consent, legitimate interest, contractual necessity, legal obligation, or one of the other bases recognized under applicable frameworks. Managing the legal basis for each category of processing, documenting it, and ensuring that the basis remains valid as processing activities evolve requires ongoing governance that most organizations underestimate.
Cookie consent and tracking technology compliance,an area that has seen significant regulatory attention and enforcement in Europe and is becoming more prominent in US state privacy frameworks,requires both technical implementation and ongoing maintenance as technology platforms and regulatory interpretations evolve.
Vendor and Third-Party Data Agreements
Privacy regulations impose accountability for personal data that is shared with or processed by third parties. Data processing agreements, standard contractual clauses for international transfers, and vendor security assessments are all required components of a privacy-compliant third-party management program. CyberSecOp's Third Party Risk Management service addresses the security dimensions of this requirement,evaluating the security posture of vendors who process personal data on the organization's behalf and ensuring that contractual security obligations are reflected in actual vendor practices.
Breach Notification Obligations
Privacy regulations impose notification obligations when personal data is involved in a security incident, with timelines that range from 72 hours under GDPR to 30 days or more under various state frameworks, and varying thresholds for what constitutes a reportable breach. Meeting these obligations requires both the technical capability to detect and investigate incidents quickly and the organizational processes to assess, document, and communicate breach information to regulators and affected individuals within required timelines. CyberSecOp's Incident Response Services integrate breach notification assessment into the incident response workflow, ensuring that regulatory obligations are identified and met as part of the response process rather than as an afterthought.
Security Requirements as Privacy Requirements
Most privacy regulations require that personal data be protected by appropriate technical and organizational security measures, a requirement that directly connects privacy compliance to cybersecurity program maturity. Demonstrating adequate security to a privacy regulator requires documented security controls, evidence of their implementation, and records of ongoing assessment and improvement. CyberSecOp's managed security services provide both the security controls and the documentation that privacy compliance programs require, connecting the cybersecurity program to the privacy compliance function in a way that eliminates duplication and ensures consistency.
How an MSSP Structures the Compliance Program
Compliance Gap Assessment
The starting point for any structured compliance program is an honest assessment of current state against applicable requirements. CyberSecOp's Cybersecurity Assessment Services include privacy-specific evaluation,mapping the organization's data flows, processing activities, and security controls against the requirements of applicable regulations and identifying the gaps that represent the greatest compliance risk.
Framework-Based Security Program Development
Rather than building separate compliance programs for each applicable regulation, an MSSP implements a security and privacy program grounded in a comprehensive framework,NIST, ISO 27001, or a purpose-built privacy framework, that satisfies the requirements of multiple regulations simultaneously. Controls implemented for GDPR adequacy frequently satisfy the security requirements of US state privacy laws, HIPAA, and PCI DSS with appropriate documentation, eliminating the redundancy of regulation-by-regulation compliance building.
Ongoing Monitoring and Regulatory Tracking
Privacy compliance is not static. Regulations are amended, enforcement guidance is updated, court decisions change the interpretation of existing requirements, and new legislation continues to emerge. An MSSP with dedicated compliance expertise monitors these developments and translates them into actionable adjustments to the client's compliance program,ensuring that the program remains current without requiring the client to maintain a full-time regulatory monitoring function.
Virtual CISO for Privacy and Compliance Governance
Privacy compliance requires executive-level accountability, a designated privacy officer function, board-level reporting on compliance status, and the authority to implement required changes to business processes and technology systems. CyberSecOp's Virtual CISO Program provides this governance function for organizations that cannot support a dedicated privacy and security executive, ensuring that compliance obligations are owned at the leadership level and reflected in organizational priorities and resource allocation.
The Cost of Non-Compliance Is Rising
Privacy regulation enforcement is no longer a distant risk that organizations can reasonably treat as low probability. GDPR penalties of up to four percent of global annual turnover have been imposed on organizations across a wide range of sectors. US state privacy regulators are actively investigating and penalizing non-compliant businesses. The SEC is enforcing its cybersecurity disclosure rules with real consequences. And the reputational and litigation exposure that follows a high-profile privacy failure frequently exceeds the regulatory penalty itself.
Organizations that have treated privacy compliance as a legal department concern rather than an operational program are increasingly discovering that this framing is insufficient for the regulatory environment of 2026. Compliance requires security controls, data management capabilities, vendor oversight, and incident response processes that span the entire organization. Contact CyberSecOp at cybersecop.com/contact to discuss how our compliance program management services can help your organization navigate the current regulatory landscape, or start with a Cybersecurity Assessment to establish where you stand today.
The Future of MSSPs: What's Next for Managed Security in the Age of AI
The managed security services industry was built on a premise that remains as valid today as it was when the first MSSPs emerged in the late 1990s: most organizations cannot build and sustain enterprise-grade security capabilities on their own. The economics of security talent, the cost of purpose-built tooling, and the complexity of the threat landscape all favor a managed services model over an entirely in-house approach. What has changed, and continues to change rapidly, is what that managed services model looks like.
The MSSP of 2026 looks substantially different from the MSSP of 2016. The perimeter-based security model that once defined the category has given way to identity-centric, cloud-native architectures. Threat detection has shifted from signature-based rules to behavioral analytics and machine learning. The talent shortage that made managed security attractive has become more acute, not less. And artificial intelligence, as both a tool for defenders and a capability for attackers, is reshaping every dimension of the security landscape. For businesses evaluating their security partnerships and strategies, understanding where the MSSP industry is heading is as important as understanding where it has been. CyberSecOp's managed security services are built on this forward-looking foundation, continuously evolving to meet the threats and requirements of tomorrow's environment, not just today's.
AI as Both Threat and Tool
No single development has had more impact on the near-term future of managed security than the rapid maturation of artificial intelligence capabilities. AI is simultaneously expanding the capabilities of defenders and lowering the barrier to entry for attackers, and MSSPs are at the center of both dynamics.
On the defensive side, AI-powered threat detection platforms are enabling security operations centers to process dramatically larger volumes of security telemetry, surface genuine threats from a sea of alerts, and identify attack patterns that rule-based systems would miss entirely. Machine learning models trained on vast datasets of malicious behavior can detect novel malware variants, identify compromised credentials through behavioral anomalies, and flag insider threats through subtle deviations from normal activity patterns. The result is a security operations capability that is more accurate, faster, and more scalable than any purely human-driven approach.
On the offensive side, the same AI capabilities are enabling attackers to generate more convincing phishing content, automate vulnerability discovery, produce malware that evades signature-based detection, and conduct social engineering at a scale that was previously impossible. CyberSecOp's Security Operations Center has integrated AI-enhanced detection capabilities across its monitoring operations, ensuring that the defensive application of AI keeps pace with its offensive use.
The Shift to Proactive Security
From Reactive Detection to Continuous Exposure Management
The traditional MSSP model was fundamentally reactive: monitor for threats, detect when something goes wrong, and respond. The future of managed security is moving toward a more proactive posture, continuous exposure management that systematically identifies and reduces attack surface before attackers can exploit it.
Continuous Threat Exposure Management (CTEM) is an emerging framework that replaces periodic assessment with ongoing, programmatic evaluation of an organization's attack surface, vulnerability exposure, and control effectiveness. Rather than an annual penetration test and a quarterly vulnerability scan, CTEM provides a continuously updated picture of security posture that enables prioritized, risk-driven remediation. CyberSecOp's Attack Surface Management and Vulnerability Management Service are building blocks of this approach, providing the continuous external and internal visibility that CTEM requires.
Threat Intelligence as a Managed Service
Threat intelligence, actionable information about adversary tactics, techniques, and infrastructure, has historically been available to large enterprises with dedicated intelligence teams and the budget to access premium feeds. The future of the MSSP model includes industrialized threat intelligence that is contextualized, operationalized, and delivered as part of the managed service, providing every client organization with the same quality of adversary knowledge that was previously reserved for the largest security organizations.
This means not just knowing that a particular threat actor is active, but understanding which of that actor's techniques are relevant to a specific client's environment, which assets they are most likely to target, and what defensive actions would be most effective against their known playbook. CyberSecOp's Dark Web Monitoring service is one component of this intelligence layer, providing visibility into threat actor activity specifically relevant to client organizations.
Zero Trust Becomes the Operational Standard
Zero Trust, the security model that rejects implicit trust based on network location and requires continuous verification of every user, device, and application seeking access to resources, has moved from a conceptual framework to an implementation standard. The future of managed security is built on Zero Trust architecture as a baseline rather than an advanced option.
For MSSPs, this means helping client organizations implement and operate the identity, device management, and network segmentation controls that Zero Trust requires, and continuously monitoring the policy enforcement mechanisms that make Zero Trust effective in practice. CyberSecOp's network security practice designs Zero Trust architectures appropriate for each client's environment and manages the ongoing enforcement and monitoring that keeps the model effective as the environment evolves.
The Expanding Scope of Managed Security
Cloud Security Posture Management
As organizations migrate workloads to cloud environments and adopt multi-cloud architectures, the security posture of cloud infrastructure has become a primary concern. Misconfigured cloud storage buckets, overly permissive identity policies, and unmonitored cloud-native services have been responsible for some of the largest data exposures of recent years. Cloud Security Posture Management, the continuous assessment and remediation of cloud configuration against security best practices, is becoming a standard component of managed security services, not an optional add-on.
OT and IoT Security
The convergence of information technology and operational technology, accelerated by industrial IoT deployments, smart city infrastructure, healthcare device connectivity, and manufacturing automation, is expanding the scope of what managed security must cover. MSSPs that can provide security operations across both IT and OT environments, using protocols and monitoring approaches appropriate for industrial control systems alongside those used for conventional IT infrastructure, will be substantially better positioned to serve the needs of asset-heavy industries than those limited to traditional IT security.
Application Security Integration
As organizations develop software more rapidly and deploy it more frequently, the integration of security into the development pipeline, DevSecOps, is becoming a managed service rather than an internal capability. MSSPs that can provide application security testing, secure code review, and software composition analysis as part of a continuous deployment pipeline extend their value into the development lifecycle, not just the operational environment. CyberSecOp's penetration testing services already encompass application security testing, a capability that is increasingly being delivered as a continuous, integrated service rather than a periodic engagement.
Managed Detection and Response Evolution
Managed Detection and Response has matured significantly as a service category, moving from alert forwarding and basic triage to genuinely active threat hunting, automated response playbook execution, and deep forensic investigation capability. The future of MDR includes increasingly automated response to well-understood threat patterns, freeing human analysts to focus on novel, complex, and high-judgment investigations. CyberSecOp's managed detection and response capabilities are built on this automation-augmented analyst model.
The Talent Challenge and the AI Response
The cybersecurity talent shortage is structural, not cyclical. The gap between the number of security professionals needed and the number available has persisted for years and shows no sign of closing through conventional workforce development alone. AI is the most significant near-term response to this challenge, not by replacing security analysts, but by dramatically amplifying what each analyst can do.
AI-assisted security operations enable analysts to investigate more alerts with greater depth, to identify patterns across larger datasets than any human team could process manually, and to automate the routine triage and documentation that consumes a disproportionate share of analyst time. The result is a security operations center that delivers more with the same or fewer human resources, directly addressing the economics that make managed security valuable in the first place.
For client organizations, this means that the quality of managed security services will increasingly be differentiated not just by the number of analysts an MSSP employs, but by the sophistication of the AI platforms those analysts work with and the quality of the data those platforms are trained on. CyberSecOp's investment in AI-augmented security operations reflects this reality, ensuring that the analysts working on client environments have the most effective tools available.
What Businesses Should Do to Prepare
The evolution of the managed security landscape has direct implications for how businesses should evaluate and structure their security partnerships. Several priorities are worth focusing on as the industry develops.
Businesses should assess whether their current managed security partner has genuine AI-augmented detection capabilities or is still operating a primarily rules-based SOC. The difference in detection effectiveness against modern threats is substantial and growing.
Organizations should evaluate their readiness for Zero Trust implementation, not as a future project but as an active transition with a defined roadmap. The architectural changes required are significant, and the organizations that begin earlier will be better positioned as Zero Trust requirements become more explicit in regulatory frameworks and procurement requirements.
Compliance obligations will continue to expand in scope and specificity. Businesses that have not built a structured compliance program, one that maps their security controls to applicable regulatory requirements and maintains that mapping as regulations evolve, will face increasing exposure as enforcement intensifies.
Finally, organizations should ensure that their security partnership includes strategic oversight, not just operational execution. The technical landscape is changing too rapidly for a security program that lacks executive-level direction and regular strategic review to remain effective. CyberSecOp's Virtual CISO Program provides this strategic layer, ensuring that security strategy keeps pace with both the threat landscape and the business's own evolution.
The MSSP of Tomorrow Is Being Built Today
The managed security services industry is in a period of substantial transformation. The organizations that will lead the next decade of the industry are those investing now in AI-augmented operations, proactive exposure management, expanded OT and cloud security capabilities, and the compliance program management that the regulatory environment increasingly demands.
CyberSecOp is building that future, integrating emerging capabilities into a managed security platform that provides clients with protection that evolves alongside the threats they face. Whether you are evaluating your current security partnership, planning a Zero Trust transition, or building a compliance program for the current regulatory environment, we are ready to help. Contact us at cybersecop.com/contact or begin with a Cybersecurity Assessment to understand where your program stands today and where it needs to go.
The Role of MSSPs in Securing Smart Cities from Cyber Threats
A traffic management system reroutes emergency vehicles through congested streets in real time. A water treatment plant adjusts chemical dosing levels automatically based on sensor readings. A power grid balances load across thousands of distributed generation sources without human intervention. These are not future scenarios, they are operational realities in cities around the world today. They are also networked, software-driven systems that can be attacked.
Smart city infrastructure represents a new category of attack surface that sits at the intersection of information technology, operational technology, and public safety. When a corporate network is breached, the consequences are measured in data loss, financial damage, and reputational harm. When the networked systems that control a city's power supply, water treatment, transportation network, or emergency services are compromised, the consequences can extend to public health and physical safety at a population scale. The organizations responsible for protecting this infrastructure, whether municipal governments, utilities, transit authorities, or the private operators who increasingly manage these systems on their behalf, require the kind of continuous, expert-led security program that a Managed Security Services Provider (MSSP) is positioned to deliver.
What Makes Smart City Infrastructure a Distinct Security Challenge
Smart city systems are not simply IT systems at a larger scale. They combine traditional information technology, servers, networks, applications, and cloud platforms, with operational technology: the industrial control systems, programmable logic controllers, sensors, and actuators that interact directly with the physical world. Securing this combined environment requires expertise that spans both domains, and the security posture of most smart city deployments reflects the historical divide between IT and OT security disciplines.
Operational technology was designed for reliability and longevity, not for networked connectivity or cybersecurity. Industrial control systems that were isolated from external networks for decades have been progressively connected to city management platforms and cloud analytics services, gaining operational efficiency while inheriting connectivity risks they were never designed to address. Many of these systems run legacy software with known vulnerabilities that cannot be patched without disrupting services that operate continuously. Updating windows that a corporate IT team would measure in hours may require weeks of planning in a water treatment or power distribution context.
The consequence of a successful attack on operational technology is also categorically different from a conventional data breach. A ransomware attack that encrypts city administrative systems is serious. A cyberattack that manipulates the chemical dosing controls of a water treatment plant, as occurred in Oldsmar, Florida in 2021, is a public health emergency. CyberSecOp's Risk Assessment Services address smart city environments by evaluating risk across both IT and OT domains, identifying the assets where a compromise would carry the most severe consequences and prioritizing protection accordingly.
The Smart City Attack Surface
Transportation and Traffic Management Systems
Connected traffic management infrastructure, adaptive signal control systems, variable message signs, tunnel and bridge monitoring, parking management platforms, and connected vehicle communication networks, is managed through networked control systems that present multiple external attack vectors. A compromised traffic management system could be used to create gridlock during an emergency response, disable tunnel ventilation systems, or manipulate variable speed limits on highways in ways that create physical danger.
Smart transit systems, including automated train control, passenger information systems, ticketing infrastructure, and fleet management platforms, carry their own connectivity risks. Ransomware attacks against transit agencies have disrupted ticketing systems and operational communications in major cities, with consequences ranging from passenger inconvenience to meaningful operational disruption.
Energy and Utilities Infrastructure
Smart grid technology enables more efficient energy distribution, renewable energy integration, and real-time demand management, and it connects components of the electrical grid that were previously isolated to networks that can be reached from external environments. Advanced metering infrastructure, distribution of automation systems, and energy management platforms create an expanded attack surface across the energy sector.
Water and wastewater systems represent a particularly high-consequence target. Treatment processes rely on industrial control systems that manage chemical addition, filtration, and distribution, systems where unauthorized access and manipulation can have direct public health consequences. CyberSecOp's Compliance Security Consulting team works with water sector organizations to implement security programs aligned with EPA cybersecurity guidance and the America's Water Infrastructure Act requirements.
Public Safety and Emergency Services
Emergency communications systems, the networks that carry 911 calls, dispatch communications, and first responder coordination, are attractive targets for attackers seeking to maximize disruption during a crisis. Attacks that disable or degrade emergency communications at the moment they are most needed represent a severe public safety threat. Computer-aided dispatch systems, records management platforms, and body-worn camera networks have all been targeted in ransomware attacks against law enforcement and emergency services organizations.
Surveillance and public safety camera networks present both an attack surface and a data sensitivity concern. Compromised camera systems can be used to monitor law enforcement activity, manipulate footage, or serve as a pivot point into broader city network infrastructure. The personal data these systems collect, including biometric data from facial recognition platforms, carries significant regulatory implications under state and federal privacy law.
Smart Buildings and Municipal Facilities
City-owned buildings, municipal offices, courthouses, libraries, transit stations, and public venues, increasingly rely on networked building management systems that control heating, ventilation, air conditioning, access control, elevators, and fire suppression. These systems are connected to city networks and managed remotely, creating pathways between building infrastructure and broader municipal IT environments. A compromised building management system can be used to manipulate physical access controls, create uncomfortable or unsafe environmental conditions, or serve as a lateral movement point into adjacent city networks.
Connected Sensors and IoT Infrastructure
Smart cities deploy thousands of sensors across their environments, air quality monitors, noise sensors, parking availability detectors, waste level indicators, flood sensors, and environmental monitoring equipment. Each of these devices is a networked endpoint with its own firmware, authentication requirements, and update lifecycle. Many IoT devices deployed in smart city contexts run embedded software that is difficult or impossible to update in the field, creating persistent vulnerability exposure across large device populations.
The Threat Actor Landscape
Smart city infrastructure attracts a range of threat actors whose motivations and capabilities vary significantly. Nation-state actors with strategic interests in disrupting an adversary's civil infrastructure represent the highest-capability threat, documented pre-positioning activity by state-sponsored groups in energy grid and water sector networks has been reported by U.S. and allied government agencies. Ransomware operators target municipalities because local governments often have limited security maturity, operational continuity requirements that create pressure to pay quickly, and constrained IT budgets that have historically resulted in unpatched systems.
Hacktivists targeting city infrastructure to make political statements, insider threats from current or former employees with knowledge of critical systems, and opportunistic attackers exploiting exposed vulnerabilities complete the threat picture. CyberSecOp's Security Operations Center monitors threat intelligence across all of these actor categories, providing early warning of campaigns targeting municipal and critical infrastructure environments.
How an MSSP Secures Smart City Infrastructure
IT and OT Security Integration
The most significant structural gap in smart city security is the divide between IT security teams, who manage networks, servers, and applications, and the OT engineers who manage industrial control systems and critical infrastructure. Effective smart city security requires unified visibility across both environments. CyberSecOp's managed security program bridges this divide, providing monitoring, threat detection, and incident response capabilities that span conventional IT infrastructure and the specialized OT systems that directly interact with physical city operations.
Continuous Monitoring and Threat Detection
Smart city environments generate enormous volumes of network traffic and system telemetry across a highly heterogeneous device population. Making sense of this data, identifying the signals of malicious activity against a background of normal operational variation, requires both sophisticated analytics and experienced human analysts. CyberSecOp's Security Operations Center provides 24/7 monitoring across smart city environments, with detection capabilities tuned to the specific protocols, traffic patterns, and attack techniques relevant to both IT and OT infrastructure.
Vulnerability Management Across the Device Ecosystem
The diversity of devices, operating systems, and protocols in a smart city environment makes vulnerability management substantially more complex than in a conventional enterprise setting. CyberSecOp's Vulnerability Management Service adapts to this complexity, maintaining a comprehensive asset inventory, tracking vulnerability exposure across all device categories, and coordinating remediation in a way that accounts for the operational constraints of systems that cannot be patched on a standard enterprise schedule.
Network Segmentation and Access Control
Limiting the blast radius of a successful intrusion requires network architecture that prevents free lateral movement between system categories. Critical infrastructure control systems should be isolated from administrative networks, public-facing services, and connected citizen applications through well-designed segmentation that restricts communication to what is operationally necessary. CyberSecOp's network security practice designs and implements segmentation architectures appropriate for smart city environments, ensuring that a compromise in one system cannot cascade into adjacent critical infrastructure.
Incident Response for Critical Infrastructure Events
When a cyberattack affects smart city infrastructure, the response must account for both the cybersecurity dimensions of the incident and its potential physical consequences. CyberSecOp's Incident Response Services are structured for critical infrastructure contexts, with pre-planned response procedures, coordination with relevant government agencies including CISA and sector-specific information sharing organizations, and the ability to escalate from cybersecurity containment to physical safety mitigation when the nature of the attack requires it.
Compliance with Critical Infrastructure Frameworks
Smart city operators are subject to a growing body of regulatory requirements specific to critical infrastructure sectors. NERC CIP standards apply to electric utility systems. The EPA's cybersecurity requirements govern water sector organizations. CISA's cross-sector guidance addresses shared risks across critical infrastructure categories. CyberSecOp's Compliance Security Consulting team helps municipal governments and infrastructure operators build compliance programs that satisfy sector-specific requirements while establishing a coherent, unified security posture across all city systems.
Supply Chain Security for Smart City Technology
Smart city deployments depend on technology vendors, systems integrators, and managed service providers across a complex supply chain. Each of these relationships introduces risk, a compromised vendor's software update, a hardware component with an embedded backdoor, or a systems integrator with inadequate security practices can all serve as entry points into city infrastructure. CyberSecOp's Third Party Risk Management service evaluates the security posture of smart city technology suppliers and service providers, ensuring that procurement and integration decisions account for security risk alongside technical and commercial criteria.
The Stakes Are Higher Than in Any Enterprise Environment
The cybersecurity challenges of smart city infrastructure are not simply a larger version of enterprise security challenges. The physical consequences of a successful attack, the operational constraints on patching and remediation, the diversity of systems and protocols, and the public accountability that attaches to government-operated infrastructure all make this a uniquely demanding security environment.
Municipal governments and infrastructure operators that approach smart city security as an extension of their existing IT security program will find it insufficient. Those that engage a managed security partner with specific expertise in both IT and OT environments, critical infrastructure threat actors, and the regulatory frameworks governing city operations will be substantially better positioned to protect the systems their residents depend on. Contact CyberSecOp at cybersecop.com/contact to discuss how our managed security services apply to your smart city security program, or begin with a Cybersecurity Assessment to establish your current posture.
Cybersecurity for Smart Vehicles: How MSSPs Protect Connected Cars from Hacking
The modern automobile is no longer primarily a mechanical system. It is a networked computing platform on wheels — running tens of millions of lines of software, communicating continuously with cloud infrastructure, receiving over-the-air updates, and interacting with smartphones, charging networks, toll systems, and roadside infrastructure. The cybersecurity implications of that transformation are significant, and the automotive industry is only beginning to grapple with them at the scale the problem demands.
Connected vehicles collect and transmit an extraordinary volume of data — location history, driving behavior, biometric patterns, passenger information, and real-time vehicle diagnostics. They execute software that controls physical systems — braking, acceleration, steering, and collision avoidance — where a security failure is not a data breach but a potential physical safety event. And they operate within complex supply chains where software and hardware components from dozens of vendors are integrated into systems that must function reliably for a decade or more. Managing cybersecurity risk across this environment requires the kind of structured, continuous program that a Managed Security Services Provider (MSSP) is built to deliver.
The Expanding Attack Surface of the Connected Vehicle
Early automobiles had no external network connectivity. Compromising one required physical access to the vehicle. Modern connected vehicles communicate across multiple interfaces simultaneously — and each interface represents a potential attack vector.
Cellular connectivity enables over-the-air software updates, remote diagnostics, and cloud-connected infotainment services. Bluetooth connects smartphones, headsets, and accessories. Wi-Fi enables hotspot functionality and dealership diagnostic access. Vehicle-to-everything (V2X) communication protocols enable interaction with roadside infrastructure, other vehicles, and traffic management systems. USB ports provide media and device connectivity. The onboard diagnostics (OBD-II) port — present in virtually every vehicle manufactured since the mid-1990s — provides direct access to vehicle network data and, in some cases, control systems.
Each of these connectivity points is an entry vector that an attacker could potentially exploit to access the vehicle's internal network. CyberSecOp's Attack Surface Management methodology applies directly to connected vehicle environments — continuously mapping the interfaces, communications, and third-party integrations that define the total attack surface of a vehicle fleet or automotive platform.
The Internal Architecture: CAN Bus and Beyond
Inside a modern vehicle, electronic control units (ECUs) — specialized computers that manage individual vehicle systems — communicate over internal networks. The most widely used of these is the Controller Area Network (CAN bus), a protocol designed in the 1980s for reliability in industrial environments, not for security in networked ones. CAN bus lacks authentication — any device connected to the network can send messages to any other device, and there is no mechanism to verify that a message comes from a legitimate source.
This architectural characteristic means that an attacker who gains access to the vehicle's internal network through any external interface — a compromised cellular modem, a malicious USB device, a vulnerable infotainment system — can potentially send commands to critical vehicle systems. Demonstrated attacks in research settings have shown that remote access to infotainment systems can, through the internal network, affect braking and steering on vehicles that have not addressed this architectural vulnerability.
Real-World Attack Vectors and Documented Threats
Over-the-Air Update Exploitation
Over-the-air (OTA) software update capability is one of the most significant advances in automotive software management — allowing manufacturers to patch vulnerabilities, add features, and resolve issues without requiring a dealership visit. It is also a high-value attack target. A compromised OTA update pipeline could distribute malicious firmware to an entire vehicle fleet simultaneously, affecting every vehicle that accepts the update before the compromise is detected.
Securing OTA update infrastructure requires cryptographic signing of update packages, integrity verification before installation, and robust monitoring of the update distribution pipeline — controls that mirror those applied to traditional enterprise software update systems but must account for the physical safety implications of a compromised update in an automotive context.
Telematics and Connected Services Attacks
Telematics systems — the cellular-connected modules that enable remote vehicle monitoring, emergency services, and fleet management — are a well-documented attack surface. Vulnerabilities in telematics server infrastructure, in the APIs that connect mobile applications to vehicle systems, and in the telematics module firmware itself have been demonstrated by security researchers. A compromised telematics system can expose precise vehicle location data, enable remote commands, and serve as an entry point into the vehicle's broader network.
For fleet operators and automotive manufacturers, telematics security is not just a vehicle issue — it is an enterprise security issue. The servers and APIs that manage fleet telematics are corporate assets that require the same security controls as any other internet-facing infrastructure.
Infotainment System Vulnerabilities
The infotainment system — the touchscreen display and associated computing hardware that manages navigation, media, phone connectivity, and increasingly a wide range of vehicle settings — runs complex software on general-purpose hardware that is connected to both external networks and the vehicle's internal CAN bus. Vulnerabilities in infotainment software have been the entry point for several significant automotive security research demonstrations, and the long lifecycle of vehicles means that infotainment systems may run software that is years behind current patch levels.
Smartphone and Third-Party Application Integration
The integration of smartphones with vehicle systems through CarPlay, Android Auto, and proprietary manufacturer platforms creates a bidirectional connectivity relationship with implications for both vehicle and device security. A malicious application on a connected smartphone may be able to interact with vehicle systems in unintended ways. Conversely, a compromised vehicle infotainment system may be able to access data on a connected phone — contacts, messages, location history, and application data — that the vehicle owner did not intend to share with the vehicle's systems.
Charging Infrastructure Attacks
Electric vehicle charging infrastructure introduces an additional attack surface: the communication protocol between the vehicle and the charging station. The Combined Charging System (CCS) and other charging protocols include data communication capabilities that have been demonstrated to carry vulnerabilities. A compromised charging station could potentially deliver malicious firmware to a connected vehicle — a threat that becomes more significant as charging infrastructure expands and standardizes.
Physical Interface Exploitation
The OBD-II port — required by regulation to be accessible for emissions testing and diagnostics — provides direct access to vehicle network data and is present in an easily accessible location in most vehicles. Aftermarket OBD-II dongles, insurance telematics devices, and fleet tracking hardware connected to this port have been demonstrated to carry vulnerabilities that provide remote network access to any attacker who can reach the device's wireless interface. A compromised OBD-II device in a vehicle is functionally equivalent to a compromised network device in an enterprise environment — providing persistent, internal network access from outside the vehicle's physical perimeter.
The Regulatory and Standards Landscape
Automotive cybersecurity is increasingly regulated. The United Nations Economic Commission for Europe's WP.29 regulations — which apply to vehicles sold in Europe, Japan, South Korea, and other participating markets — require manufacturers to implement cybersecurity management systems covering the entire vehicle lifecycle, from design through production to post-sale operation and decommissioning. ISO/SAE 21434, the international standard for road vehicle cybersecurity engineering, provides the technical framework for implementing these requirements. For fleet operators, automotive suppliers, and technology companies building connected vehicle services, demonstrating compliance with these frameworks is becoming a market access requirement as well as a security best practice. CyberSecOp's Compliance Security Consulting team helps automotive industry participants build compliance programs aligned with WP.29, ISO 21434, and applicable data privacy regulations.
How an MSSP Secures Connected Vehicle Environments
Vehicle and Fleet Security Assessments
A structured security assessment of a connected vehicle environment evaluates attack surfaces across all connectivity interfaces, internal network architecture, software update mechanisms, cloud backend infrastructure, and third-party integrations. CyberSecOp's Cybersecurity Assessment Services and Threat and Vulnerability Assessments apply proven assessment methodology to the automotive context — identifying the highest-risk attack vectors and providing a prioritized remediation roadmap.
Penetration Testing of Vehicle Systems and Backend Infrastructure
Connected vehicle security requires testing across multiple domains simultaneously — vehicle-side interfaces and ECU firmware, telematics and OTA update infrastructure, mobile applications, and cloud backend systems. CyberSecOp's penetration testing services encompass all of these layers, providing the comprehensive attack simulation that identifies exploitable vulnerabilities before adversaries discover them independently.
Continuous Monitoring of Fleet and Backend Infrastructure
The servers, APIs, and data pipelines that support connected vehicle services are enterprise infrastructure — and they require continuous monitoring for anomalous access patterns, unauthorized configuration changes, and indicators of compromise. CyberSecOp's Security Operations Center provides 24/7 monitoring across connected vehicle backend environments, integrating vehicle fleet telemetry with conventional infrastructure monitoring to provide a unified threat detection capability.
Incident Response for Automotive Security Events
When a cybersecurity incident affects connected vehicle systems — whether a telematics breach, a compromised OTA update, or an active attack on fleet management infrastructure — the response must account for both conventional IT security considerations and the physical safety implications unique to the automotive context. CyberSecOp's Incident Response Services provide immediate containment and forensic investigation capabilities, coordinated with vehicle manufacturers and regulatory authorities where the nature of the incident requires it.
Supply Chain Security for Automotive Software
Modern vehicles incorporate software components from dozens of suppliers. Each component represents a potential supply chain attack vector — a vulnerability in a supplier's software development environment, a compromised open-source dependency, or a malicious modification introduced before delivery. CyberSecOp's Third Party Risk Management service evaluates the security posture of automotive software suppliers and technology partners, extending security oversight across the supply chain that feeds vehicle software development.
Data Privacy and Compliance Program Development
Connected vehicles generate personal data at scale — precise location histories, driving behavior profiles, biometric authentication data, and passenger information. Managing this data in compliance with GDPR, CCPA, and other applicable privacy regulations requires a formal data governance program that addresses collection, retention, access controls, and breach notification obligations. CyberSecOp's Compliance Security Consulting practice helps automotive businesses build privacy compliance programs that satisfy regulatory requirements across all markets in which they operate.
Security Must Be Built In, Not Bolted On
The automotive industry has learned from the broader technology sector that security cannot be effectively added to a product after the fact. The vulnerabilities that have been demonstrated in connected vehicle systems are largely the result of security being treated as an afterthought in architectures designed primarily for functionality. The industry's regulatory moment — driven by WP.29, ISO 21434, and increasing regulatory interest in automotive data privacy — is forcing a shift toward security-by-design that will take years to fully implement across existing vehicle fleets.
In the interim, fleet operators, automotive suppliers, telematics providers, and connected mobility businesses face a security landscape that is complex, rapidly evolving, and consequential in ways that extend beyond data loss to physical safety. A managed security program provides the continuous oversight, structured assessment, and incident response capability that this environment demands.
Contact CyberSecOp at cybersecop.com/contact to discuss how our managed security services can be applied to your connected vehicle security program, or begin with a Cybersecurity Assessment to establish a clear picture of your current risk posture.
How MSSPs Prevent and Detect Business Email Compromise (BEC) Attacks
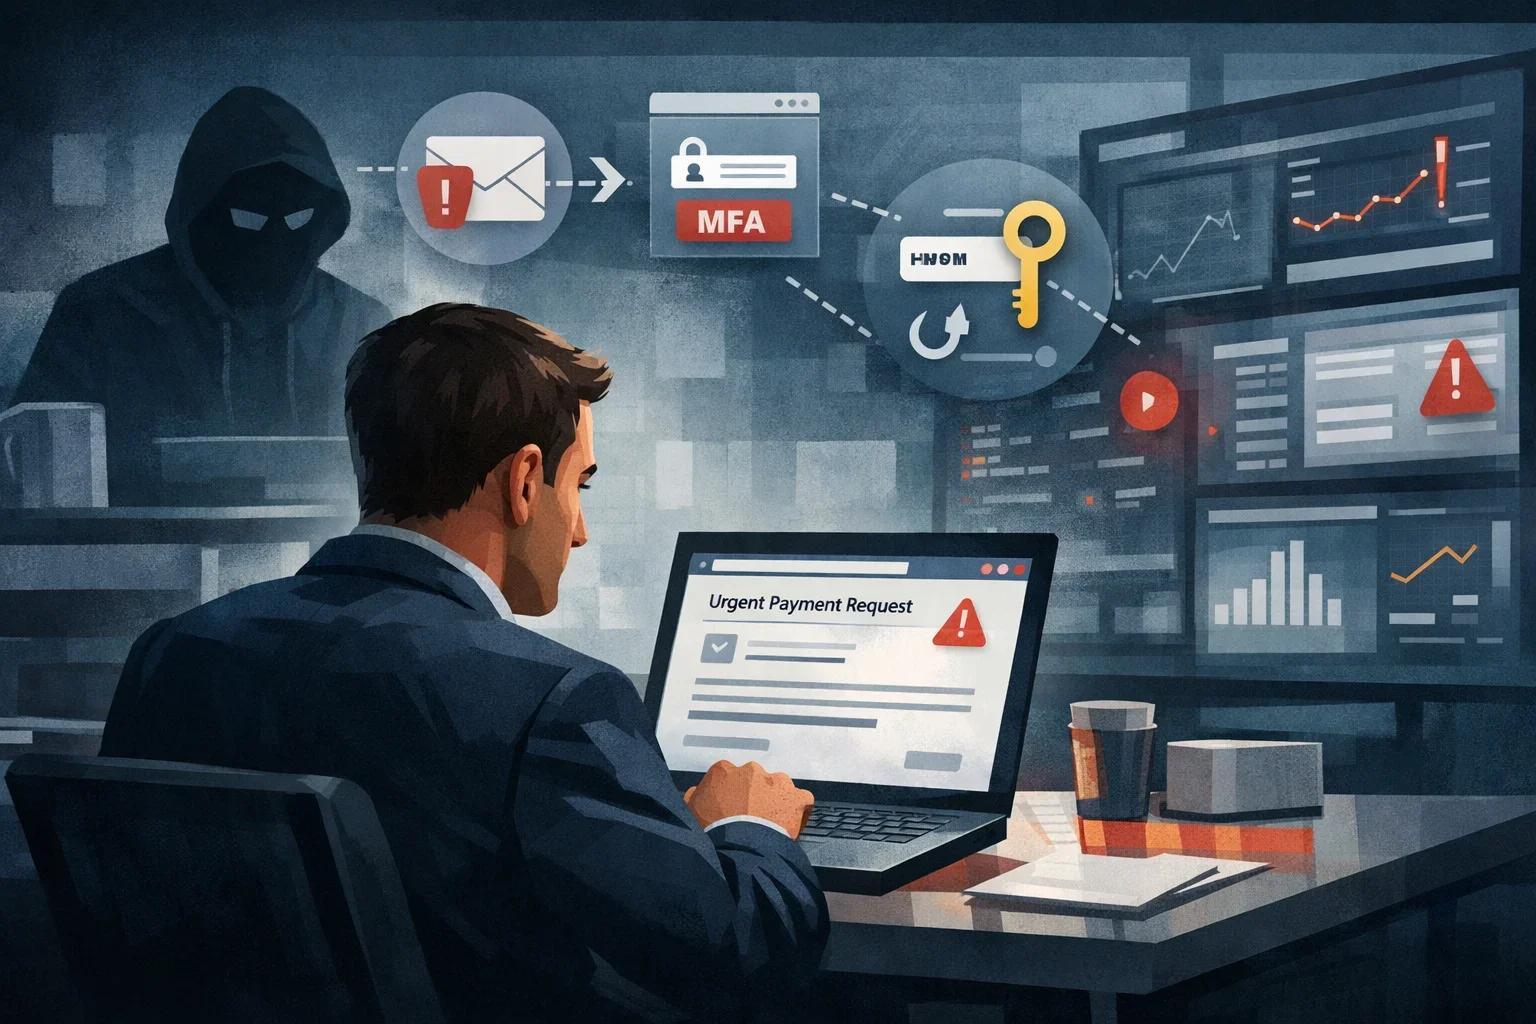
A finance manager receives an urgent email from the CEO. The message is direct, professional, and consistent with the executive's writing style. It requests a wire transfer to a new vendor account — time-sensitive, confidential, not to be discussed with others. The finance manager processes the transfer. The money is gone within minutes, irretrievably routed through a chain of accounts designed to defeat recovery efforts. The CEO never sent the email.
Business Email Compromise is not a sophisticated technical exploit. It does not require the attacker to breach a firewall, plant malware, or circumvent complex security controls. It requires only a convincing email and a recipient who trusts it. That simplicity is precisely what makes it so effective — and so expensive. The FBI's Internet Crime Complaint Center has consistently ranked BEC among the costliest categories of cybercrime, with losses measured in the billions of dollars annually across organizations of every size and industry. A Managed Security Services Provider (MSSP) addresses BEC through a layered combination of technical controls, process enforcement, and continuous monitoring that individual organizations struggle to sustain on their own.
Understanding How BEC Attacks Work
BEC attacks succeed by exploiting two things that organizations cannot simply turn off: trust in executive communications and pressure to act quickly on time-sensitive requests. Attackers invest significant effort in the reconnaissance phase — studying an organization's leadership structure, understanding financial workflows, identifying the employees with payment authorization, and observing communication patterns that allow them to craft messages that feel authentic.
The attack itself may take several forms depending on what the attacker has learned about the target. What unites them is the exploitation of human judgment under pressure, combined with technical spoofing or account compromise that makes the communication appear legitimate.
The Primary BEC Attack Patterns
CEO Fraud and Executive Impersonation
The most widely recognized BEC variant involves an attacker impersonating a senior executive — typically the CEO, CFO, or another officer with authority to direct financial activity — and sending a fraudulent payment request to an employee in accounts payable, finance, or treasury. The message typically conveys urgency, requests confidentiality, and discourages the recipient from following normal verification procedures by framing them as unnecessary bureaucracy or a time constraint.
These emails may be sent from a domain that is visually similar to the legitimate corporate domain — a technique called typosquatting — or from a free webmail account with a display name matching the executive's. In more sophisticated attacks, the executive's actual email account has been compromised, and the fraudulent request arrives from the legitimate address.
Vendor and Invoice Fraud
In vendor impersonation BEC, attackers research an organization's existing supplier relationships and send fraudulent payment instructions that appear to come from a known vendor. The message typically advises that the vendor's banking details have changed and requests that future payments be directed to a new account. Because the request references a real vendor relationship and real outstanding invoices, it bypasses the skepticism that might greet a message from an unknown sender.
This attack variant is particularly difficult to detect because it does not require impersonating an internal executive — the fraudulent communication mimics an external relationship that finance staff interact with regularly.
Account Compromise-Based BEC
The most damaging BEC attacks begin with an actual compromise of a legitimate email account — typically through phishing, credential stuffing, or malware that captures login credentials. With access to a real inbox, attackers can monitor ongoing communications, identify pending transactions, and intervene at precisely the right moment with fraudulent payment instructions that appear to come from the verified, trusted account. Compromised accounts also allow attackers to set up forwarding rules that provide persistent visibility into communications even after the initial access point is addressed. CyberSecOp's Dark Web Monitoring service provides early warning when employee credentials appear in breach databases — enabling password resets before compromised credentials can be used to access corporate email.
Payroll Diversion
Payroll diversion attacks target HR and payroll departments rather than finance teams. An attacker impersonates an employee and requests a change to their direct deposit banking information — redirecting their next payroll disbursement to an attacker-controlled account. Because payroll change requests are routine and expected, they may receive less scrutiny than large wire transfer requests. The losses per incident are typically smaller than in CEO fraud cases, but the volume of potential targets within any organization is significantly larger.
Attorney and Legal Impersonation
In this variant, attackers impersonate attorneys or legal representatives — often claiming to be handling a confidential acquisition, compliance matter, or regulatory investigation that requires an urgent and discreet financial transaction. The authority and urgency implied by legal involvement, combined with the confidentiality framing that discourages consultation with colleagues, makes this a particularly effective social engineering approach against executives who might otherwise apply more scrutiny.
Why BEC Is So Difficult to Stop Without a Managed Program
BEC attacks are effective precisely because they work with the grain of normal business operations rather than against it. Wire transfers happen. Payment instructions change. Executives make urgent requests. Vendors update their banking details. The attacker's task is to make a fraudulent communication indistinguishable from a legitimate one — and in many cases, they succeed.
Technical controls alone cannot fully address this. A sophisticated BEC email sent from a compromised legitimate account will pass email authentication checks. An impersonation sent from a carefully crafted lookalike domain may evade filters that are not configured to detect subtle domain variations. And even when technical controls flag a suspicious message, a recipient under pressure may override the warning and act anyway.
Effective BEC defense requires a combination of technical controls that make impersonation harder, monitoring that identifies anomalous financial activity and suspicious email patterns, process controls that enforce verification procedures regardless of apparent urgency, and employee awareness that prepares staff to recognize and respond correctly to BEC attempts.
How an MSSP Prevents and Detects BEC
Email Authentication and Domain Protection
The technical foundation of BEC prevention is email authentication — a set of standards that allow receiving mail servers to verify that an email claiming to come from a given domain actually originated from an authorized sender for that domain. SPF, DKIM, and DMARC are the three primary standards, and their effective deployment requires careful configuration and ongoing monitoring to prevent both spoofing of the organization's own domain and to ensure that fraudulent emails impersonating the organization are rejected rather than delivered.
An MSSP deploys and maintains email authentication standards across the organization's domain portfolio — including secondary domains that may be less carefully managed than the primary domain. CyberSecOp also monitors for the registration of lookalike and typosquatting domains that attackers commonly use in BEC campaigns, providing early warning through its Attack Surface Management service before those domains are used in active attacks.
Advanced Email Security and BEC-Specific Filtering
Standard spam and phishing filters are insufficient for BEC detection because many BEC emails contain no malicious links or attachments — the attack payload is the text of the message itself. Advanced email security platforms use natural language processing, behavioral analysis, and communication graph analysis to identify BEC-pattern emails based on the characteristics of the request rather than the presence of technical indicators of compromise.
These controls detect impersonation attempts by analyzing display name spoofing, domain similarity, sender reputation, and communication patterns that deviate from an employee's established relationship history. Managed and continuously tuned as part of CyberSecOp's Managed Security Services, these filters are updated against current BEC campaign techniques rather than static rule sets that attackers quickly learn to circumvent.
Account Takeover Detection and Response
Detecting a compromised email account — one that an attacker is using for BEC from within the legitimate inbox — requires behavioral monitoring that identifies usage patterns inconsistent with the account owner's normal activity. Logins from unexpected geographies, access at unusual hours, mass email reading or forwarding rule creation, and communication pattern anomalies are all indicators of account compromise that CyberSecOp's Security Operations Center monitors for across the organization's email environment. When a compromised account is identified, rapid response limits the window during which the attacker can use it for BEC or other fraudulent activity.
Financial Transaction Monitoring and Controls
BEC prevention requires controls that extend beyond the email channel into the financial workflow itself. An MSSP works with organizations to implement process controls that enforce verification requirements for financial transactions regardless of the apparent authority or urgency of the request — out-of-band confirmation for payment instruction changes, dual-approval workflows for wire transfers above defined thresholds, and callback verification procedures that use known, pre-established contact information rather than details provided in the suspicious communication.
These procedural controls are the last line of defense when technical controls have been bypassed — and they are the controls that most frequently prevent BEC losses that would otherwise be unrecoverable.
Targeted Security Awareness Training
Finance staff, executives, HR personnel, and anyone with payment authorization authority are the primary targets of BEC campaigns. Generic phishing awareness training is insufficient preparation for the specific social engineering techniques used in BEC attacks. CyberSecOp's Security Awareness Training programs include BEC-specific content and simulated BEC exercises — exposing staff to realistic attack scenarios that build recognition and correct response behaviors before a real attack tests those skills. Training emphasizes the critical importance of verification procedures and establishes a clear organizational norm: urgency and confidentiality requests are themselves warning signs, not reasons to bypass controls.
Incident Response When BEC Succeeds
When a BEC attack results in a fraudulent transfer, the speed of response is the primary determinant of how much of the loss can be recovered. The FBI's Financial Fraud Kill Chain — a rapid notification process involving the sending financial institution, the FBI, and the receiving bank — has a meaningful success rate when initiated within hours of a fraudulent transfer. After 72 hours, the probability of fund recovery drops dramatically. CyberSecOp's Incident Response Services are structured to activate immediately when a BEC event is identified — initiating the recovery notification chain, preserving forensic evidence, containing any associated email account compromise, and coordinating with law enforcement where appropriate.
vCISO-Level Policy and Governance
BEC prevention requires organizational policy changes — authorization thresholds, verification requirements, and communication protocols — that need executive sponsorship and consistent enforcement to be effective. CyberSecOp's Virtual CISO Program provides the strategic leadership to develop, implement, and maintain these policies as part of a coherent financial fraud prevention program, ensuring that process controls keep pace with evolving BEC techniques.
The Human Factor Cannot Be Engineered Away
BEC is fundamentally a human attack — it succeeds by exploiting trust, authority, and urgency in ways that bypass both technical controls and rational scrutiny. No technology eliminates this attack surface entirely. What a managed security program does is make impersonation technically harder, make suspicious patterns visible before a transfer is completed, and build the organizational culture and process discipline that causes employees to pause, verify, and escalate rather than act under pressure.
The organizations that successfully resist BEC campaigns are those that have invested in all three layers — technical controls, monitoring, and human preparedness — and have maintained them as a continuous program rather than a one-time deployment. Begin with a Cybersecurity Assessment to evaluate your current BEC risk posture across email security, financial controls, and employee awareness. Contact CyberSecOp at cybersecop.com/contact to speak with a member of our team.
Hackers Targeting AI Models: How MSSPs Defend Machine Learning Systems from Cyber Threats
Hackers Targeting AI Models: How MSSPs Defend Machine Learning Systems from Cyber Threats
Businesses are deploying machine learning systems to make consequential decisions — approving loan applications, flagging fraudulent transactions, diagnosing medical images, routing customer service inquiries, and filtering security alerts. Those decisions are only as trustworthy as the models that produce them. Attackers have taken notice, and a growing body of research and real-world incident data confirms that AI and machine learning systems are not just tools for defenders. They are also targets.
The security discipline surrounding AI and machine learning systems — often called adversarial machine learning or AI security — addresses a set of threats that have no direct equivalent in traditional cybersecurity. Attackers can manipulate a model's outputs without ever accessing its code. They can poison the data a model learns from. They can extract proprietary intellectual property from a deployed model through nothing more than a series of carefully constructed queries. For businesses that have integrated AI into operational or customer-facing workflows, these are not theoretical risks. They are active attack vectors that a Managed Security Services Provider (MSSP) with emerging technology expertise is uniquely positioned to address.
Why AI Systems Require a Different Security Approach
Traditional software security focuses on protecting code, data, and infrastructure from unauthorized access or modification. AI systems introduce an additional attack surface: the model itself — its parameters, its training data, its decision boundaries, and the assumptions baked into its design. An attacker who cannot breach the server hosting a machine learning model may still be able to manipulate its outputs, extract its logic, or corrupt its future behavior through the data it continues to learn from.
The consequences of a compromised AI system depend entirely on what that system controls. A manipulated fraud detection model may silently approve fraudulent transactions. A poisoned malware classifier may learn to treat malicious files as benign. A model used in hiring or lending decisions may be manipulated to produce discriminatory outcomes that expose the organization to regulatory and legal liability. CyberSecOp's Risk Assessment Services help organizations understand which of their AI-dependent workflows carry the greatest risk exposure and prioritize security investment accordingly.
How Attackers Target Machine Learning Systems
Adversarial Input Attacks
Adversarial inputs are carefully crafted data points designed to cause a machine learning model to produce an incorrect output — while appearing entirely normal to a human observer. The classic demonstration involves images that are imperceptibly modified at the pixel level, causing an image classifier to confidently misidentify the subject. In operational contexts, adversarial inputs have been demonstrated against malware classifiers that can be fooled into treating malicious files as benign, network intrusion detection systems that can be evaded by subtly modifying attack traffic, and facial recognition systems that can be confused by specific patterns of makeup or printed accessories.
For businesses whose security controls rely on machine learning-based detection — and most modern endpoint protection, email security, and network monitoring platforms do — adversarial input attacks represent a meaningful threat to the reliability of those controls.
Data Poisoning
Machine learning models are only as reliable as the data they are trained on. Data poisoning attacks corrupt the training dataset — either by injecting malicious samples that teach the model to behave incorrectly, or by subtly modifying legitimate training data to introduce exploitable biases into the model's decision-making. Poisoning attacks can be particularly difficult to detect because the model continues to perform well on most inputs while exhibiting manipulated behavior on specific, attacker-controlled trigger conditions — a property known as a backdoor.
For organizations that train models on continuously ingested data — including threat intelligence systems that learn from new malware samples or fraud detection models that learn from transaction history — data poisoning represents an ongoing operational risk that requires active monitoring of training pipelines and data sources.
Model Extraction and Intellectual Property Theft
A trained machine learning model can represent significant intellectual property — the product of large investments in data collection, labeling, computational resources, and engineering expertise. Model extraction attacks systematically query a deployed model and use the responses to reconstruct a functionally equivalent copy, without ever accessing the underlying parameters or training data. An attacker with access to a public API for a proprietary model can extract a working approximation through a sufficient volume of queries — stealing the intellectual property without triggering any conventional security alert.
For businesses whose competitive advantage is embedded in proprietary AI systems — recommendation engines, predictive analytics platforms, automated underwriting models — model extraction is a direct threat to the value of that investment.
Model Inversion and Privacy Attacks
Model inversion attacks exploit the relationship between a model's outputs and its training data to reconstruct sensitive information about individuals in that dataset. A model trained on personal health records, for example, may inadvertently encode information about specific patients in its parameters — information that can be partially recovered through carefully constructed queries. For businesses subject to data privacy regulations, a model inversion attack may constitute a data breach even if the underlying training data was never directly accessed.
Supply Chain Attacks on AI Components
The machine learning ecosystem relies heavily on open-source frameworks, pre-trained models, and third-party datasets — each of which represents a potential supply chain attack vector. Malicious code injected into a widely used machine learning library, a pre-trained model distributed with a hidden backdoor, or a poisoned public dataset incorporated into training pipelines can compromise AI systems at scale before the attack is identified. CyberSecOp's Third Party Risk Management service extends vendor risk assessment to the AI supply chain — evaluating the provenance and integrity of the models, datasets, and libraries that organizational AI systems depend on.
Prompt Injection Against Large Language Models
Organizations deploying large language models in customer-facing or internal applications face a specific attack category: prompt injection. Malicious users craft inputs designed to override the model's system instructions, bypassing content restrictions, extracting confidential information from the model's context, or causing the model to perform actions outside its intended scope. As enterprises integrate language models with internal systems — databases, email platforms, code repositories, and document management tools — the consequences of a successful prompt injection expand proportionally with the model's level of access.
Regulatory and Compliance Dimensions of AI Security
Regulatory scrutiny of AI systems is intensifying across sectors. Financial services regulators are examining model risk management frameworks for machine learning-based decision systems. Healthcare regulators are evaluating the safety and reliability requirements for AI-assisted clinical tools. The European Union's AI Act introduces risk-based compliance requirements for AI systems used in high-stakes applications. Organizations that fail to demonstrate that their AI systems are secure, explainable, and resistant to manipulation face both regulatory exposure and reputational risk. CyberSecOp's Compliance Security Consulting team helps businesses build AI governance frameworks that satisfy emerging regulatory requirements while maintaining operational flexibility.
How an MSSP Defends Machine Learning Systems
AI Security Assessments and Red Team Testing
Defending an AI system begins with understanding how it can be attacked. CyberSecOp's Cybersecurity Assessment Services include AI-specific evaluation — testing models for adversarial input vulnerabilities, assessing training pipeline security, reviewing data provenance and integrity controls, and evaluating the access controls governing model parameters and inference APIs. Red team exercises simulate realistic attacker behavior against deployed AI systems, identifying exploitable weaknesses before adversaries discover them.
Training Data Integrity and Pipeline Security
Protecting the integrity of training data requires controls at every stage of the data pipeline — from collection and labeling through storage, preprocessing, and ingestion into the training process. An MSSP implements data provenance tracking, anomaly detection on training datasets, and access controls that prevent unauthorized modification of training data or model parameters. For systems that learn continuously from operational data, monitoring for distribution shifts and unexpected changes in model behavior provides an early warning signal for potential poisoning activity.
Adversarial Robustness Testing
Making models more resistant to adversarial inputs requires systematic testing — generating adversarial examples across a range of attack techniques and evaluating the model's behavior on each. An MSSP with AI security expertise integrates adversarial robustness testing into the model development lifecycle, identifying vulnerabilities before deployment and establishing ongoing testing cadences that track robustness as models are retrained and updated.
API Security and Query Rate Controls
Deployed machine learning models exposed through APIs require the same security controls as any other web service — authentication, authorization, input validation, and rate limiting — plus additional controls specific to the AI context. Query rate limiting and anomaly detection on API usage patterns can identify model extraction attempts before sufficient queries have been made to reconstruct the model. CyberSecOp's network security and application security practices apply these controls to AI inference APIs as a standard component of deployment security review.
Continuous Monitoring of Model Behavior
Machine learning models can be compromised without any change to the underlying code or infrastructure. Monitoring for unexpected shifts in model outputs — decisions that deviate from historical patterns, confidence scores that cluster in unusual ranges, or outputs that correlate with specific input characteristics — provides behavioral detection coverage that infrastructure monitoring alone cannot deliver. CyberSecOp's Security Operations Center extends this monitoring capability to AI-specific telemetry, integrating model behavior analytics into the broader threat detection program.
Incident Response for AI System Compromises
When an AI system is compromised — whether through a poisoning attack, an adversarial input campaign, or a model extraction event — the response requires both conventional incident response capabilities and AI-specific expertise. CyberSecOp's Incident Response Services address the full scope of AI system incidents: identifying the extent of compromise, assessing the integrity of training data and model parameters, determining what outputs may have been affected during the compromise period, and establishing remediation procedures that restore trustworthy model behavior.
AI Is an Asset and an Attack Surface
Machine learning systems create genuine business value — and they introduce genuinely new categories of security risk. As AI deployment expands across industries and use cases, the security discipline surrounding these systems will become as foundational as the security of the networks and endpoints that host them.
Organizations that invest in AI security now build on a growing body of best practices, frameworks, and tooling that makes their AI systems more trustworthy, more resilient, and more defensible to regulators and clients alike. A Cybersecurity Assessment from CyberSecOp will evaluate your AI security posture across model integrity, training pipeline security, API controls, and compliance readiness. Contact us at cybersecop.com/contact to speak with a member of our team.
Cybersecurity in the Legal Industry: Why Law Firms Need MSSP Protection
Law firms sit at the intersection of two things that make them among the most attractive targets in the threat landscape: they hold extraordinarily sensitive client information, and they have historically underinvested in cybersecurity. That combination has not gone unnoticed by attackers.
The legal industry manages some of the most confidential data in existence, merger and acquisition details before public announcement, litigation strategies, privileged communications, personal financial records, and proprietary intellectual property. A breach that exposes any of this does not just harm the firm. It harms clients, triggers regulatory consequences, generates civil liability, and can permanently damage a firm's reputation in a profession built entirely on trust. Yet many law firms, particularly small and mid-sized practices, continue to operate without the security controls that the sensitivity of their data demands. A Managed Security Services Provider (MSSP) with legal industry expertise addresses this gap in a way that no general IT provider can replicate.
Why Law Firms Are High-Value Targets
Attackers understand the legal sector's value proposition better than many law firms understand their own risk profile. A successful breach of a large firm's systems may yield confidential information about dozens of corporate clients simultaneously, making law firms a highly efficient target compared to attacking each of those clients individually.
Several characteristics of the legal profession compound this exposure. Attorney-client privilege means that sensitive communications are voluminous and rarely scrutinized by outside parties, creating large archives of high-value data that may sit unprotected for years. The billable hour model creates pressure to minimize non-revenue overhead, which historically has included IT and security investment. And the legal profession's reliance on email as its primary communication channel makes phishing a particularly effective attack vector against lawyers and their staff.
Nation-state actors target law firms working on cross-border transactions, trade disputes, and government matters. Organized cybercriminals target firms for ransomware attacks, knowing that the time-sensitive nature of legal proceedings creates enormous pressure to pay quickly. Insider threats, from disgruntled employees, departing partners, or compromised credentials, represent an ongoing concern in an environment where access to sensitive files is broad by operational necessity. CyberSecOp's Risk Assessment Services help law firms understand their specific threat profile and prioritize accordingly.
The Regulatory Landscape for Legal Cybersecurity
Law firms operate under a web of professional responsibility obligations, data privacy regulations, and client contractual requirements that create significant compliance complexity around cybersecurity.
State bar associations across the country have interpreted existing rules of professional conduct to impose affirmative cybersecurity obligations on attorneys. The duty of competence, long understood to require legal knowledge and skill, has been extended by most bars to encompass the technical competence necessary to protect client information in digital form. The duty of confidentiality requires lawyers to make reasonable efforts to prevent unauthorized disclosure of client information, a standard that is increasingly being interpreted through a cybersecurity lens.
Beyond professional responsibility, law firms handling personal data are subject to state privacy laws including the California Consumer Privacy Act, the New York SHIELD Act, and equivalent legislation in other jurisdictions. Firms with healthcare clients must understand their exposure under HIPAA's business associate framework. Those working with financial institutions may be subject to SEC and FTC data security requirements. CyberSecOp's Compliance Security Consulting team maps these overlapping obligations into a coherent compliance framework that law firms can implement and demonstrate to clients and regulators alike.
The Most Significant Threats Law Firms Face
Ransomware and Data Extortion
Ransomware attacks against law firms have become a defining threat of the past several years. Attackers encrypt firm systems and demand payment for restoration, but the more damaging evolution of this attack type involves exfiltrating sensitive client data before encryption and threatening to publish it if the ransom is not paid. For a law firm, the prospect of privileged client communications appearing on a dark web leak site is often more catastrophic than the operational disruption of the encryption itself.
Ransomware response requires both prevention and preparedness. CyberSecOp's Incident Response Services provide law firms with pre-negotiated response capabilities, ensuring that when an attack occurs, containment begins immediately rather than hours into the incident while a firm tries to identify who to call.
Business Email Compromise
Business email compromise attacks targeting law firms most commonly manifest as wire fraud. Attackers monitor email communications, often following a phishing-based inbox compromise, and intervene at the moment a real estate closing, settlement payment, or transaction escrow is being arranged, redirecting funds to attacker-controlled accounts. Law firms have lost millions of dollars to individual BEC incidents, and the fraudulent wire transfers are frequently unrecoverable.
Effective defense requires both technical controls, email authentication standards, advanced phishing filtering, and anomaly detection on financial communications, and procedural safeguards that require out-of-band verification for any changes to payment instructions.
Third-Party and Supply Chain Risk
Law firms rely on a broad ecosystem of third-party technology providers, document management platforms, e-discovery vendors, legal research tools, client portal software, and cloud storage services. Each of these relationships represents a potential pathway into the firm's environment if the vendor's security is inadequate. CyberSecOp's Third Party Risk Management service evaluates the security posture of legal technology vendors, ensuring that a weakness in a third party's environment cannot become a breach of client confidentiality.
Insider Threats and Access Governance
The legal profession's high-turnover environment, lateral partner moves, associate attrition, staff transitions, creates persistent access governance challenges. Departing employees with broad file access and no prompt offboarding process represent a meaningful data exfiltration risk. Former staff with active credentials are a well-documented threat vector that firms consistently underestimate.
Robust access governance means ensuring that access rights are provisioned based on role and matter assignment, reviewed regularly, and revoked immediately upon departure, not when someone remembers to submit a helpdesk ticket.
Phishing and Spear Phishing
Attorneys receive a high volume of unsolicited communications from unknown parties as a normal part of legal practice, making them particularly susceptible to phishing attacks that mimic legitimate client inquiries, court notifications, or opposing counsel correspondence. AI-generated phishing messages that incorporate accurate case details, jurisdiction-specific language, and appropriate legal terminology are increasingly difficult to distinguish from legitimate communications. CyberSecOp's Security Awareness Training programs are tailored to the specific phishing patterns that target legal professionals, building recognition skills that generic training programs do not address.
How an MSSP Delivers Legal-Specific Security
24/7 Monitoring Through a Dedicated SOC
Legal matters rarely conform to business hours. A ransomware attack initiated on a Friday evening, timed to exploit the gap between end-of-week and Monday morning, is a documented attacker tactic against professional services firms. CyberSecOp's Security Operations Center provides continuous monitoring across law firm environments, detecting and responding to threats regardless of when they occur, without relying on internal staff who may not be available outside business hours.
Email Security and Anti-Phishing Controls
Given that email is the primary attack surface for law firms, hardening it is among the highest-priority security investments available. This includes deploying email authentication standards that prevent domain spoofing, implementing advanced filtering that identifies phishing attempts based on behavioral and contextual signals rather than simple keyword matching, and establishing secure client communication portals that reduce reliance on unencrypted email for sensitive matter communications.
Endpoint Protection for Remote and Mobile Work
Attorneys work everywhere, courthouses, client offices, airports, and home offices. The devices they use outside the firm's network perimeter carry the same sensitive data as systems inside it, and they face additional exposure from public networks and unsecured environments. CyberSecOp's endpoint protection capabilities ensure that every device used for legal work is monitored, encrypted, and capable of remote wipe if lost or stolen, protecting client confidentiality regardless of where work happens. For firms whose attorneys travel frequently, this connects directly to CyberSecOp's broader network security program.
Data Loss Prevention
Controlling the movement of sensitive data, preventing it from being emailed to personal accounts, uploaded to unauthorized cloud storage, or transferred to removable media, is a foundational control for any firm managing privileged communications. Data loss prevention tools monitor and enforce policies around data movement, generating alerts when behavior is inconsistent with normal patterns and blocking high-risk transfers before they result in exposure.
Dark Web Monitoring for Exposed Firm Data
Law firm credentials, client data, and internal documents periodically surface on dark web forums, either from direct breaches of the firm or from breaches of third-party services used by firm personnel. CyberSecOp's Dark Web Monitoring service continuously scans these sources for the firm's domain, email addresses, and associated data, providing early warning that allows compromised credentials to be reset before they are used in an attack.
Virtual CISO for Legal Security Strategy
Most law firms do not have a Chief Information Security Officer, and the firms that do often have a single individual whose departure would leave the program without strategic leadership. CyberSecOp's Virtual CISO Program provides law firms with experienced security leadership that develops and maintains a security program aligned with professional responsibility obligations, client contractual requirements, and applicable data privacy regulations, without the cost or continuity risk of a single full-time hire.
Client Trust Is the Firm's Most Valuable Asset
Every client who retains a law firm does so with an implicit expectation that their most sensitive matters will be protected. A cybersecurity failure does not just create legal and regulatory exposure, it breaks the foundational trust that the attorney-client relationship depends on. In a profession where reputation is built over decades and can be destroyed overnight, the cost of a preventable breach is difficult to overstate.
Begin with a Cybersecurity Assessment to understand your firm's current risk posture across email security, endpoint protection, access governance, and compliance readiness. CyberSecOp's legal industry security consulting practice works exclusively with the challenges and obligations unique to the legal profession. Contact us at cybersecop.com/contact to speak with a member of our team.
Smartphone Security: How MSSPs Prevent Mobile Device Hacks
The device that holds your email, your authenticator app, your VPN client, your corporate documents, and your calendar is also the device most likely to be lost, stolen, connected to an untrusted network, and left outside your organization's security perimeter for the majority of every working day. That device is the smartphone — and for most businesses, it is both the most widely used corporate tool and the least consistently secured one.
Mobile devices have become the primary computing environment for a significant portion of the workforce. Sales teams manage client relationships from their phones. Executives approve transactions and access financial systems on mobile. Field staff submit reports, access operational systems, and communicate with headquarters entirely through smartphones and tablets. The security implications of this shift are substantial — and most organizations have not kept pace with the risk. A Managed Security Services Provider (MSSP) provides the mobile security infrastructure and oversight that ensures these devices extend your security program rather than undermine it.
Why Mobile Devices Are a Growing Attack Surface
Several characteristics of smartphones make them a particularly attractive target for attackers. They are always on, always connected, and carry a combination of personal and corporate data that provides attackers with both immediate value and a pathway into broader organizational systems. Unlike corporate laptops that are managed, monitored, and periodically patched by IT teams, mobile devices often operate in a governance gap — used for corporate purposes but without corporate security controls.
The bring-your-own-device (BYOD) model, which is common across industries and company sizes, compounds this problem. When employees use personal smartphones for work, the organization has limited visibility into what other applications are installed, what networks the device connects to, and whether the device's operating system is current. A personal device that is also a corporate device inherits both the individual user's security habits and the organization's risk.
CyberSecOp's Cybersecurity Assessment Services consistently identify mobile devices as one of the most significant unmanaged risk areas in organizational security programs — even in businesses that have invested heavily in perimeter and endpoint security for traditional workstations.
The Mobile Threat Landscape
Malicious Applications
App stores — even official platforms — have repeatedly been used to distribute malware. Applications that request excessive permissions, impersonate legitimate tools, or contain hidden malicious functionality have reached millions of devices before being identified and removed. Once installed, a malicious application may harvest credentials, monitor communications, access the device's camera and microphone, or serve as a persistent backdoor into the device's data.
The risk is magnified when employees install applications from outside official app stores — sideloading applications that have bypassed platform security review entirely. Corporate mobile security policies must address both the applications approved for installation and the controls that prevent unauthorized software from reaching corporate devices.
Phishing via SMS, Messaging Apps, and Email
Mobile phishing — sometimes called smishing when delivered via SMS — has grown substantially as attackers recognize that mobile users are more likely to act impulsively on links received through messaging channels than on those received via desktop email. Text messages carry an implicit sense of urgency and familiarity that email does not, and the smaller screen of a mobile device makes it harder to inspect URLs before tapping them.
Beyond SMS, phishing attacks now routinely arrive through WhatsApp, Teams, Slack, LinkedIn messaging, and other platforms that employees use on their phones. Many of these channels bypass email security filters entirely, delivering malicious links directly to a device that may have no filtering controls in place at all.
Unsecured Wi-Fi and Network Attacks
Smartphones automatically connect to previously used networks and are frequently connected to public Wi-Fi in hotels, airports, cafes, and conference centers. The risks associated with these connections — man-in-the-middle attacks, evil twin networks, and packet interception — apply equally to mobile devices as to laptops. A device that employees would never connect to public Wi-Fi without a VPN on their laptop is routinely connected without any protection on their phone. CyberSecOp addresses mobile network security as part of its broader network security program, ensuring that VPN enforcement extends to mobile devices and not just traditional endpoints.
OS and Application Vulnerabilities
Mobile operating systems and the applications running on them contain vulnerabilities — some of which are actively exploited before patches are available. Zero-day exploits targeting iOS and Android have been used in targeted attacks against high-value individuals, and known vulnerabilities in popular applications are routinely exploited against devices that have not applied available updates. The challenge for organizations is that mobile OS update cycles are controlled by device manufacturers and carriers, not by IT teams, and employees frequently delay or decline updates.
SIM Swapping
SIM swapping attacks involve an attacker convincing a mobile carrier to transfer a victim's phone number to a SIM card the attacker controls. Once successful, the attacker receives all calls and SMS messages intended for the victim — including the one-time passcodes used for SMS-based multi-factor authentication. SIM swapping has been used to bypass MFA on corporate accounts, cryptocurrency wallets, and financial platforms, with losses frequently in the hundreds of thousands of dollars per incident.
Physical Loss and Device Theft
The simplest mobile security risk is also among the most common: a device that is lost or stolen. A smartphone without full-disk encryption, a strong screen lock, and remote wipe capability is a portable repository of corporate data and authentication credentials that requires no technical expertise to exploit. In regulated industries, a lost unencrypted device carrying client or patient data may itself constitute a reportable breach event.
Stalkerware and Unauthorized Monitoring
Stalkerware — applications designed to covertly monitor device activity — can be installed on corporate devices by malicious actors who have temporary physical access to an unlocked phone. These applications operate invisibly in the background, transmitting location data, communications, and screen content to a remote party. In corporate contexts, this threat extends to competitive intelligence gathering and insider threat scenarios where a device is used to monitor an employee's communications with clients or legal counsel.
How an MSSP Secures the Mobile Environment
Mobile Device Management
Mobile Device Management (MDM) is the foundational layer of enterprise mobile security, giving organizations centralized control over every enrolled device in the fleet. Through CyberSecOp's managed security program, MDM deployment enforces encryption on all corporate data, requires screen lock authentication, manages application permissions, controls which networks devices can connect to, and enables remote wipe for lost or stolen devices — all from a centralized console that IT and security teams can monitor and act on without physical access to individual devices.
For BYOD environments, MDM can be configured to apply corporate security policies exclusively to a containerized work profile while leaving personal data and applications untouched — addressing the privacy concerns that frequently cause employee resistance to device management enrollment.
Mobile Threat Defense
Mobile Threat Defense (MTD) solutions extend endpoint detection and response capabilities to mobile devices, continuously analyzing device behavior, application activity, network connections, and operating system integrity for indicators of compromise. Where traditional antivirus approaches are inadequate for mobile environments, MTD identifies threats based on behavioral patterns — detecting malicious applications, network-based attacks, and OS-level compromises in real time. CyberSecOp's Security Operations Center monitors MTD alerts across the mobile fleet alongside traditional endpoint and network telemetry, ensuring that a compromise detected on a smartphone triggers the same response workflow as one detected on a server.
Application Vetting and Control
An MSSP establishes and enforces corporate application policies — defining which applications are approved for installation on corporate or managed devices, blocking access to known malicious or high-risk applications, and monitoring for applications that have been approved but subsequently identified as problematic. For organizations developing their own mobile applications, CyberSecOp's application security practice includes mobile-specific security testing that identifies vulnerabilities before they reach production.
Zero Trust Mobile Access
Zero Trust Network Access extends least-privilege principles to mobile devices — ensuring that a smartphone connecting to corporate resources must continuously verify its identity, health status, and authorization before access is granted. A device that fails a compliance check — because its OS is out of date, its screen lock has been disabled, or it is connecting from an unexpected location — is denied access or placed in a restricted network segment until the issue is resolved. This control is particularly valuable for organizations with BYOD environments, where device compliance cannot be assumed. CyberSecOp implements Zero Trust mobile access as part of its broader network security architecture practice.
Security Awareness Training for Mobile Threats
The technical controls that protect mobile devices are significantly more effective when employees understand the threats they face. CyberSecOp's Security Awareness Training programs include mobile-specific content — covering smishing recognition, safe app installation practices, public Wi-Fi hygiene, physical device security, and the proper steps to take when a device is lost, stolen, or behaving unexpectedly. Employees who understand why these controls exist are far more likely to comply with them and to report anomalies promptly.
Incident Response for Mobile Compromises
When a mobile device is compromised — whether through malware infection, credential theft, physical loss, or a SIM swap attack — the response must be fast and coordinated. CyberSecOp's Incident Response Services include mobile-specific response procedures: remote device isolation and wipe, credential revocation across connected accounts, forensic preservation of device data where legally required, and investigation of how the compromise occurred and what data may have been exposed.
Mobile Security Is Not a Feature — It Is a Program
The most common mobile security failure is not a missing tool — it is the absence of a coherent program. MDM deployed without enforcement policies is ineffective. MTD deployed without SOC integration generates alerts that go unreviewed. Application controls without employee education are worked around rather than complied with.
An MSSP brings the program structure that individual tools cannot provide on their own — integrating mobile security controls into a managed security ecosystem with continuous monitoring, clear policies, employee training, and tested incident response procedures.
A Cybersecurity Assessment from CyberSecOp will evaluate your current mobile security posture, identify gaps in device management, network protection, and application controls, and produce a prioritized roadmap for closing them. Contact us at cybersecop.com/contact to speak with a member of our team.
The Future of Passwordless Authentication: How MSSPs Implement Advanced Identity Verification
The password has been the dominant form of digital authentication for more than six decades. It has also been the source of more security failures than any other single control in the history of information technology. Stolen passwords, reused passwords, weak passwords, and phished passwords account for the majority of credential-based breaches, a category that represents the most common initial access vector in cyberattacks worldwide. The security industry has known about this problem for decades. The shift away from passwords is finally underway.
Passwordless authentication, the use of cryptographic keys, biometrics, hardware tokens, and device-based verification to confirm identity without a shared secret, is moving from a niche innovation to an enterprise standard. Major technology platforms, identity providers, and regulatory frameworks are actively accelerating this transition. For businesses navigating the shift, a Managed Security Services Provider (MSSP) provides the technical expertise, implementation support, and ongoing management that makes passwordless authentication a practical reality rather than an aspirational goal.
Why Passwords Have Failed
The fundamental problem with passwords is that they are a shared secret, a piece of information known to both the user and the authenticating system. Shared secrets can be stolen, guessed, phished, intercepted in transit, extracted from breached databases, and reused across systems. No amount of password policy complexity, minimum length requirements, mandatory special characters, forced rotation schedules, has meaningfully reduced the incidence of credential compromise. In many cases, complexity requirements have made the problem worse by pushing users toward predictable substitution patterns and password reuse across personal and professional accounts.
The scale of the problem is significant. Billions of credential pairs from past data breaches circulate on dark web markets and criminal forums, available for purchase and use in credential stuffing attacks against any organization whose employees reused exposed passwords. Multi-factor authentication has provided meaningful protection against credential stuffing, but it has not eliminated the underlying vulnerability. A phished MFA code, a SIM swap attack, or an adversary-in-the-middle proxy can defeat many common MFA implementations.
CyberSecOp's Dark Web Monitoring service provides ongoing visibility into whether your organization's credentials have been exposed in third-party breaches, but monitoring for exposure is a reactive control. Passwordless authentication eliminates the credential itself as an attack surface.
How Passwordless Authentication Works
Passwordless authentication replaces the shared secret model with public-key cryptography. Rather than storing a password on a server that could be breached, a passwordless system stores a public key that is mathematically useless without the corresponding private key, which never leaves the user's device. Authentication occurs through a cryptographic challenge-response exchange that proves possession of the private key without transmitting it.
The user experience of this process typically involves a biometric, a fingerprint scan or facial recognition, or a hardware token that unlocks the private key and completes the authentication. From the user's perspective, logging in requires a touch of a finger or a glance at a camera rather than typing and remembering a complex string of characters.
The security properties of this model are substantially stronger than password-based authentication. There is no credential to steal from a server database. There is no secret to phish, a cryptographic challenge can only be answered by the device that holds the private key. There is no credential to reuse across systems. And the biometric or PIN that unlocks the private key is verified locally on the device rather than transmitted to a server.
The FIDO2 Standard and Passkeys
The technical foundation for most modern passwordless implementations is the FIDO2 standard, developed by the FIDO Alliance in collaboration with major technology companies. FIDO2 encompasses the WebAuthn protocol, which enables browsers and applications to use device-based cryptographic authentication, and the CTAP protocol, which defines how external hardware authenticators communicate with devices.
Passkeys, the consumer-facing implementation of FIDO2 credentials, are now supported natively by Apple, Google, and Microsoft platforms, and are accepted by a growing number of enterprise applications, identity providers, and consumer services. A passkey is a FIDO2 credential that can be synchronized across a user's devices through their platform account, providing the security properties of hardware-bound authentication with the convenience of availability across multiple devices.
For enterprises, FIDO2 hardware security keys provide the highest level of assurance, binding authentication to a physical device that must be present for login to succeed. These keys are phishing-resistant by design: the cryptographic challenge includes the domain of the site being authenticated to, making it impossible for a phishing site to capture and replay a valid authentication response.
Biometric Authentication: Capability and Considerations
Device-Bound Biometrics
The biometric verification used in most passwordless implementations, the Face ID scan, the Touch ID fingerprint, the Windows Hello facial recognition, occurs entirely on the device. The biometric template is stored in a secure enclave that cannot be accessed by the operating system or any application, and the biometric data itself never leaves the device. Authentication servers receive only a cryptographic proof that the biometric check succeeded, not the biometric data itself.
This architecture addresses the privacy and security concerns that have historically surrounded biometric authentication. A compromised server cannot expose biometric data it never received. A stolen biometric cannot be used on a different device whose secure enclave contains a different template.
Behavioral Biometrics
Beyond physical biometrics, behavioral biometrics analyze patterns in how users interact with their devices, typing rhythm, mouse movement patterns, touch pressure and gesture characteristics, and navigation behavior, to continuously verify identity throughout a session rather than only at the point of login. Behavioral biometrics can detect when a session that authenticated as a legitimate user is subsequently being operated by someone else, whether due to account takeover, session hijacking, or an insider sharing credentials.
Liveness Detection and Anti-Spoofing
Biometric authentication systems must be resistant to spoofing attacks, attempts to authenticate using a photograph, a silicone fingerprint, or a video replay of the legitimate user. Liveness detection, the ability to distinguish a live biometric input from a reproduction, is an active area of development, and the strength of liveness detection varies significantly across implementations. An MSSP evaluating passwordless authentication solutions for enterprise deployment includes liveness detection capability as a core assessment criterion.
The Enterprise Implementation Challenge
The security case for passwordless authentication is compelling. The implementation challenge is substantial. Most enterprise environments contain a complex mix of legacy applications, cloud platforms, on-premises systems, and third-party services that were built with password-based authentication in mind and require varying levels of effort to transition.
A passwordless rollout requires careful inventory of all systems requiring authentication, assessment of FIDO2 and passkey support across each, identification of legacy systems that will require alternative approaches or phased migration, selection and deployment of an identity provider platform capable of orchestrating passwordless flows across the environment, and development of recovery procedures for users who lose their authenticating device.
Without a structured implementation program, organizations frequently end up with passwordless authentication for some systems and password-based authentication for others, creating a hybrid environment that preserves many of the vulnerabilities the transition was meant to eliminate.
How an MSSP Implements and Manages Passwordless Authentication
Identity Architecture Assessment
The starting point for any passwordless implementation is a comprehensive understanding of the current identity landscape, what systems exist, how they authenticate users, which identity providers and directories are in use, and what the dependencies between them are. CyberSecOp's Risk Assessment Services establish this baseline, identifying both the technical requirements for a passwordless transition and the gaps that need to be addressed before implementation begins.
Identity Provider Selection and Deployment
Modern passwordless authentication relies on a centralized identity provider (IdP) that orchestrates authentication across all connected applications. An MSSP evaluates, selects, and deploys the identity platform appropriate for the organization's environment, whether that is a cloud-native provider, an on-premises solution, or a hybrid architecture, and configures it to enforce passwordless authentication policies across the application portfolio.
Phased Rollout and Legacy System Migration
A managed passwordless implementation is phased rather than wholesale, beginning with the highest-value, highest-risk applications and user populations and expanding systematically as the program matures. For legacy systems that cannot be immediately migrated to native FIDO2 support, an MSSP implements bridging solutions, identity proxies, reverse authentication gateways, and privileged access management integrations, that extend passwordless controls to systems that were not designed for them.
Hardware Security Key Management
For organizations requiring the highest level of authentication assurance, those in regulated industries, government contracting, or high-security environments, hardware security key programs require lifecycle management: key procurement and provisioning, enrollment, loss and replacement procedures, and decommissioning at departure. An MSSP manages this lifecycle as a program, ensuring that hardware keys are always accounted for and that no orphaned authenticators remain enrolled for departed personnel.
Continuous Monitoring and Anomaly Detection
Passwordless authentication significantly reduces the attack surface for credential-based attacks, but it does not eliminate all identity-related threats. Device compromise, insider threats, and authentication system vulnerabilities remain relevant concerns. CyberSecOp's Security Operations Center monitors authentication telemetry for anomalous patterns, logins from unexpected locations, authentication attempts on enrolled credentials from unrecognized devices, and unusual access patterns following successful authentication, providing behavioral coverage beyond the authentication event itself.
Compliance Alignment
Passwordless and phishing-resistant authentication is increasingly required rather than merely recommended by regulatory frameworks. NIST guidelines, OMB mandates for federal agencies, and PCI DSS version 4.0 requirements all reference phishing-resistant MFA as a standard for high-assurance authentication. CyberSecOp's Compliance Security Consulting team ensures that passwordless implementations are configured and documented in a manner that satisfies these requirements, supporting audit readiness alongside security improvement.
User Experience and Change Management
The success of a passwordless rollout depends as much on adoption as on technical implementation. Employees who find the new authentication experience confusing, inconvenient, or untrustworthy will find workarounds that undermine the security gains. CyberSecOp's Security Awareness Training programs support passwordless transitions with targeted user education, explaining how the technology works, why it is more secure than passwords, and how to handle common scenarios including device loss and account recovery.
The Transition Is Already Underway
Passwordless authentication is not a future technology waiting to become viable, it is a present technology that major platforms already support and that leading security frameworks already mandate for high-assurance use cases. Organizations that begin the transition now build on a growing ecosystem of compatible applications, mature identity platforms, and established implementation patterns. Those that defer will find themselves managing an increasingly isolated password-based authentication infrastructure as the industry moves on without them.
The path to passwordless authentication begins with understanding where you are today. A Cybersecurity Assessment from CyberSecOp will evaluate your current identity and authentication posture, map your application portfolio against passwordless readiness, and develop a phased implementation roadmap that delivers security improvements progressively rather than requiring a single disruptive transition. Contact us at cybersecop.com/contact to get started.
DNS Security: How Hackers Exploit Your Domain Name System and How MSSPs Stop Them
Every time someone visits your website, sends you an email, or connects to a cloud application, a quiet but critical process takes place behind the scenes. The Domain Name System, DNS, translates the human-readable addresses we type into the numerical addresses that computers use to communicate. It is one of the oldest and most fundamental layers of the internet. It is also one of the most frequently abused by attackers.
DNS was designed decades ago with functionality in mind, not security. The result is a protocol that underpins virtually all internet activity but carries significant inherent vulnerabilities, many of which remain exploitable today. For businesses, a successful DNS attack can redirect customers to fraudulent websites, intercept sensitive communications, take down critical services entirely, or serve as the entry point for a much larger breach. Understanding how these attacks work, and how a Managed Security Services Provider (MSSP) closes the gaps, is essential for any organization that depends on the internet to operate.
How the Domain Name System Works, and Why It's a Target
When a user types a web address into their browser, a DNS resolver queries a series of servers to find the corresponding IP address. This process happens in milliseconds and involves multiple points of trust, each of which represents a potential point of attack. DNS queries are typically transmitted in plain text, responses are cached without robust verification, and the system was built on an assumption of good faith that modern attackers have long since abandoned.
The sheer volume of DNS traffic, and the fact that most organizations monitor it poorly or not at all, makes it an attractive channel for attackers. CyberSecOp's Threat and Vulnerability Assessments consistently identify DNS as one of the most overlooked layers of an organization's attack surface.
Common DNS Attack Techniques
DNS Spoofing and Cache Poisoning
In a DNS cache poisoning attack, an attacker injects fraudulent DNS records into a resolver's cache, causing it to return a malicious IP address in response to legitimate queries. Users who type your company's web address are silently redirected to a fake site, one that may look identical to the real thing, where their credentials, payment data, or sensitive information can be harvested. Because the redirect happens at the DNS layer, users see no warning and have no indication that anything is wrong.
Cache poisoning attacks can affect thousands of users simultaneously and persist for hours or days, depending on how long the fraudulent record remains cached before it expires or is detected.
DNS Tunneling
DNS tunneling exploits the fact that DNS traffic is rarely blocked or deeply inspected by firewalls. Attackers embed data, commands, exfiltrated files, or malware payloads, inside DNS queries and responses, using the protocol as a covert communication channel. An attacker who has already established a foothold inside a network can use DNS tunneling to communicate with external command-and-control infrastructure, bypass data loss prevention controls, and exfiltrate sensitive data without triggering conventional security alerts.
DNS tunneling is particularly difficult to detect because the traffic looks, on the surface, like ordinary DNS activity. Detection requires behavioral analysis and pattern recognition that goes well beyond basic firewall rules.
DNS Hijacking
DNS hijacking attacks modify the DNS records of a legitimate domain, either by compromising the domain registrar account, exploiting vulnerabilities in DNS management platforms, or gaining access to the DNS server itself. Once hijacked, the domain can be pointed at attacker-controlled infrastructure, intercepting all traffic intended for the legitimate destination. Email, web traffic, and API communications can all be rerouted in this way.
In some cases, DNS hijacking is used to obtain fraudulent SSL certificates for the hijacked domain, giving the attacker a site that appears fully legitimate, complete with a padlock icon in the browser. CyberSecOp's Attack Surface Management service monitors for unauthorized changes to DNS records and certificate issuance events that can indicate a hijacking attempt.
Distributed Denial of Service via DNS (DNS DDoS)
DNS amplification is a well-established technique for launching large-scale Distributed Denial of Service attacks. By sending small DNS queries with a spoofed source address, set to the victim's IP, attackers cause DNS servers to send disproportionately large responses to the target, overwhelming its network capacity. DNS servers can amplify traffic by a factor of 70 or more, making them a highly efficient weapon for taking services offline.
For businesses that depend on website availability, customer portals, or cloud-based applications, a successful DNS DDoS attack translates directly to lost revenue, damaged reputation, and in some cases, regulatory exposure.
Domain Generation Algorithms (DGA)
Many modern malware strains use Domain Generation Algorithms to generate large numbers of seemingly random domain names that serve as communication points for command-and-control infrastructure. Because the domains change constantly and are generated algorithmically, traditional blocklists cannot keep up. DGA-based malware can maintain persistent communication channels with attacker infrastructure even as individual domains are identified and blocked.
The Business Impact of DNS Attacks
The consequences of a successful DNS attack extend well beyond temporary inconvenience. Customer data harvested through a spoofed login page carries the same regulatory liability as any other data breach. Business email compromise attacks that begin with DNS hijacking can result in fraudulent wire transfers and irreversible financial losses. Extended service outages from DNS DDoS attacks erode customer trust and violate service level agreements with enterprise clients.
For regulated industries, a DNS-related breach is subject to the same notification requirements and penalties as any other security incident. CyberSecOp's Compliance Security Consulting team helps businesses understand how DNS security intersects with their regulatory obligations under frameworks including HIPAA, PCI-DSS, and NIST.
How an MSSP Strengthens DNS Security
Individual IT teams rarely have the tooling, expertise, or bandwidth to monitor DNS traffic at the depth required to detect modern attacks. An MSSP addresses this gap through a combination of technology, continuous monitoring, and threat intelligence that no single internal team can replicate. CyberSecOp's Managed Security Services deliver DNS protection across several interconnected layers.
DNS Filtering and Protective DNS
DNS filtering blocks queries to known malicious domains before a connection is ever established, preventing malware from communicating with command-and-control servers, blocking access to phishing sites, and stopping DNS tunneling channels at the query level. Protective DNS services apply real-time threat intelligence to every DNS query across your environment, blocking threats that signature-based tools cannot detect.
DNSSEC Implementation
DNS Security Extensions (DNSSEC) add cryptographic signatures to DNS records, allowing resolvers to verify that a response has not been tampered with in transit. DNSSEC implementation requires careful configuration and ongoing maintenance, tasks that are frequently deferred or misconfigured without expert oversight. CyberSecOp manages DNSSEC deployment and validation as part of a comprehensive DNS hardening program.
Continuous DNS Traffic Monitoring
Through CyberSecOp's Security Operations Center, DNS traffic is monitored around the clock for behavioral anomalies, unusual query volumes, queries to algorithmically generated domains, tunneling patterns, and unauthorized record modifications. When suspicious activity is detected, the response team investigates and contains the threat before it can escalate.
Domain Registrar Security and Record Monitoring
Securing the DNS layer means securing the administrative accounts that control it. CyberSecOp's Risk Assessment Services evaluate the security of domain registrar accounts, DNS management platforms, and related credentials, identifying weak points before attackers can exploit them. Record monitoring alerts ensure that any unauthorized change to your DNS configuration triggers an immediate investigation.
Incident Response for DNS Attacks
When a DNS attack occurs, whether a cache poisoning event, a hijacking incident, or a DDoS campaign, rapid response is critical. Every minute that fraudulent DNS records remain active is another minute that customers are being redirected to attacker infrastructure. CyberSecOp's Incident Response Services provide immediate containment, forensic investigation, and restoration of legitimate DNS records, minimizing exposure and accelerating recovery.
DNS Security Is Not Optional
DNS is the foundation on which every online interaction your business conducts is built. Leaving it unmonitored and unprotected is the equivalent of leaving the front door open while investing heavily in interior locks. Attackers know this, and they exploit DNS precisely because so many organizations treat it as infrastructure rather than a security priority.
A Cybersecurity Assessment from CyberSecOp will evaluate your current DNS security posture, identify gaps in monitoring and configuration, and provide a prioritized roadmap for hardening this critical layer of your environment. Contact us at cybersecop.com/contact to get started.
The Role of MSSPs in Securing Cryptocurrency and Blockchain Networks
Blockchain technology promised something the financial world had rarely achieved: a transaction record that is transparent, immutable, and resistant to manipulation. For many applications, it has delivered on that promise. But the broader cryptocurrency ecosystem built on top of blockchain infrastructure has proven far more vulnerable than early proponents anticipated, not because the underlying cryptography is weak, but because the platforms, protocols, and human behavior surrounding it are not.
Cryptocurrency-related fraud, theft, and infrastructure attacks have resulted in billions of dollars in losses annually. Exchanges have been drained, smart contracts have been exploited, and private keys have been stolen through phishing attacks that would look familiar to any corporate security team. As businesses increasingly explore blockchain-based payment systems, digital asset custody, and decentralized finance applications, the question of how to secure these environments has moved from niche to urgent. A Managed Security Services Provider (MSSP) with expertise in emerging technology threats plays a critical role in helping organizations navigate this landscape safely.
Understanding the Blockchain Security Paradox
The blockchain itself, the distributed ledger that records transactions across a network of nodes, is exceptionally difficult to attack directly. Altering a confirmed transaction would require controlling more than half of the network's computing power, a feat that is economically prohibitive on major networks. This security property is genuine and meaningful.
The paradox is that almost everything surrounding the blockchain is far less secure than the blockchain itself. The wallets that hold private keys, the exchanges that facilitate trading, the smart contracts that automate transactions, the bridges that connect different blockchain networks, and the human operators who manage all of these components are all subject to conventional security vulnerabilities, and they are being exploited at scale.
How Attackers Target Cryptocurrency and Blockchain Environments
Private Key Theft and Wallet Compromise
Cryptocurrency ownership is, at its core, possession of a private key. Whoever controls the private key controls the assets, and unlike a stolen password, a stolen private key cannot be reset or revoked. Attackers pursue private keys through phishing campaigns, malware that scans for wallet files, fake wallet applications, and social engineering attacks targeting individuals with access to high-value wallets.
For businesses managing cryptocurrency reserves or offering digital asset services to clients, private key security is an existential concern. A single successful key theft can result in irreversible, unrecoverable loss.
Smart Contract Exploitation
Smart contracts are self-executing programs that run on blockchain networks, automating transactions, and enforcing agreement terms without intermediaries. They are also code, and code contains bugs. Unlike traditional software, where a discovered vulnerability can be patched, a deployed smart contract often cannot be modified. An exploited vulnerability remains exploitable until the contract is deprecated, or funds are drained.
The history of decentralized finance is marked by smart contract exploits that have resulted in losses ranging from millions to billions of dollars. These attacks often exploit logical flaws in contract design, reentrancy vulnerabilities, integer overflows, or flawed access controls, that a thorough security assessment would identify before deployment.
Exchange and Custodial Platform Attacks
Centralized cryptocurrency exchanges are high-value targets that combine large asset concentrations with the security challenges of any complex web platform. SQL injection, authentication bypass, API vulnerabilities, and insider threats have all been used to compromise exchanges. When an exchange is breached, customer funds held in hot wallets, those connected to the internet for operational purposes, are typically the first to be drained.
Even exchanges with strong security controls face persistent threats from sophisticated, well-funded threat actors who treat large platform attacks as long-term investment opportunities, conducting reconnaissance over months before executing an attack.
Blockchain Bridge Attacks
Cross-chain bridges, protocols that allow assets to be transferred between different blockchain networks, have emerged as one of the most frequently exploited components of the cryptocurrency ecosystem. Bridges hold large asset reserves and often involve complex smart contract logic that creates multiple potential attack surfaces. Several of the largest cryptocurrency thefts in recent years have targeted bridge protocols, with losses in the hundreds of millions of dollars per incident.
Cryptojacking
Cryptojacking attacks compromise business systems, servers, workstations, cloud infrastructure, and use their computing resources to mine cryptocurrency for the attacker's benefit. Unlike ransomware, cryptojacking is designed to remain undetected as long as possible, silently consuming resources and electricity while degrading system performance. For businesses operating cloud infrastructure, unauthorized crypto mining can result in significant unexpected costs before the intrusion is discovered.
CyberSecOp's Security Operations Center monitors for the behavioral signatures of cryptojacking, anomalous CPU usage, unusual outbound connections, and process behavior inconsistent with normal operations, enabling rapid detection and response.
Crypto-Specific Phishing and Social Engineering
The cryptocurrency space has spawned a distinct class of phishing attacks targeting both individual holders and organizational staff. Fake wallet interfaces, fraudulent airdrop offers, impersonated exchange support personnel, and SIM swapping attacks that defeat SMS-based two-factor authentication are all routinely used to steal credentials and assets. For businesses, business email compromise schemes that redirect cryptocurrency payments to attacker-controlled wallets represent a growing and difficult-to-reverse fraud category.
Regulatory and Compliance Dimensions
The regulatory landscape for cryptocurrency is evolving rapidly, with financial regulators in the United States and globally introducing new requirements for digital asset businesses around anti-money laundering (AML), know-your-customer (KYC), and cybersecurity controls. Businesses operating in this space face compliance obligations that are both novel and stringent. CyberSecOp's Compliance Security Consulting team helps digital asset businesses understand and satisfy these requirements, building compliance frameworks that can adapt as the regulatory environment continues to develop.
How an MSSP Secures Blockchain and Cryptocurrency Environments
Smart Contract Security Auditing
Before a smart contract is deployed to a production blockchain network, it should be subjected to rigorous security review, examining the code for logical flaws, known vulnerability patterns, and edge cases that could be exploited under adversarial conditions. CyberSecOp's application security practice applies formal auditing methodology to smart contract code, providing the kind of independent review that Threat and Vulnerability Assessments deliver for conventional software.
Private Key and Wallet Security Architecture
An MSSP with blockchain security expertise helps organizations design and implement key management architectures that minimize exposure, including hardware security modules (HSMs) for key storage, multi-signature approval workflows that prevent single-point-of-failure key compromise, and cold storage strategies for assets that do not require frequent access. These controls are complemented by strict access management policies that govern who can initiate transactions and under what conditions.
Exchange and Platform Penetration Testing
For businesses operating cryptocurrency platforms, regular penetration testing is essential for identifying vulnerabilities before attackers do. CyberSecOp's penetration testing services simulate the techniques used by real-world attackers against web applications, APIs, and network infrastructure, providing actionable findings that development and security teams can use to harden the platform before it is exploited.
Continuous Monitoring and Threat Detection
Blockchain transactions are publicly visible and permanently recorded, a unique property that creates opportunities for proactive threat detection. By monitoring on-chain activity for patterns consistent with known attack techniques, an MSSP can identify suspicious transaction flows, flag anomalous smart contract interactions, and detect unauthorized fund movements in real time. Combined with conventional network and endpoint monitoring through CyberSecOp's managed detection and response capabilities, this creates a comprehensive threat detection layer across both the blockchain and traditional infrastructure components of a crypto business.
Incident Response for Crypto-Specific Threats
The irreversibility of blockchain transactions makes incident response in this domain uniquely challenging. When cryptocurrency is stolen, it cannot be recalled. The priority of an incident response engagement is therefore to contain the breach, preventing further theft, preserving evidence for forensic investigation, and coordinating with exchanges to flag and potentially freeze stolen assets in transit. CyberSecOp's Incident Response Services are structured to address the specific requirements of cryptocurrency and digital asset incidents, including engagement with blockchain analytics platforms and law enforcement coordination where applicable.
Third-Party and Vendor Risk in the Crypto Ecosystem
Cryptocurrency businesses rely heavily on third-party infrastructure, blockchain node providers, oracle services, DeFi protocol integrations, and custodial partners. Each of these relationships introduces risk that must be assessed and managed. CyberSecOp's Third Party Risk Management service evaluates the security posture of third-party dependencies, ensuring that a weakness in a partner's environment cannot become a pathway into yours.
A Maturing Threat Landscape Demands Professional Security
The cryptocurrency and blockchain space is no longer a fringe technology sector occupied by early adopters. It is a multi-trillion-dollar asset class that institutional investors, payment processors, financial institutions, and enterprises are engaging with directly. The security standards applied to these environments must reflect that reality.
Attackers in this space are sophisticated, well-resourced, and highly motivated. The combination of irreversible transactions, pseudonymous ownership, and the novelty of the technology creates an environment where security shortcuts carry catastrophic consequences.
An MSSP brings the structure, expertise, and continuous oversight that this environment demands. Begin with a Cybersecurity Assessment to evaluate your current posture across both traditional and blockchain-specific risk dimensions. Contact CyberSecOp at cybersecop.com/contact to speak with a member of our team.
AI-Powered Chatbot Attacks: How Hackers Are Weaponizing AI Assistants
For most of the history of cybercrime, the limiting factor was scale. A skilled attacker could craft a convincing phishing email, but sending thousands of personalized, contextually appropriate versions of it required either automation that sacrificed quality or a team that sacrificed efficiency. Generative AI has changed that calculus entirely, and the implications for every organization's security posture are significant.
AI-powered chatbots and large language models are being used by businesses to improve customer service, accelerate content production, and streamline internal workflows. The same capabilities are being used by attackers to industrialize social engineering, automate vulnerability discovery, generate malware, and conduct fraud at a scale and sophistication that was not previously achievable. Understanding how attackers are weaponizing AI, and how a managed security program responds, is now a baseline requirement for security leadership.
The Threat Is Not Hypothetical
AI-generated phishing campaigns, deepfake audio used to impersonate executives in wire transfer fraud, and chatbot-driven credential harvesting attacks are all documented, active threats, not theoretical future risks. CyberSecOp's Security Operations Center tracks these emerging attack patterns as part of continuous threat intelligence operations, and the volume and sophistication of AI-assisted attacks has grown substantially over the past two years.
For businesses, the key challenge is that many existing security controls were designed for a pre-AI threat landscape. Phishing filters trained to detect grammatical errors and awkward phrasing are far less effective against AI-generated text that is fluent, contextually accurate, and indistinguishable from legitimate communication. Employee training programs that teach staff to spot 'obvious' phishing need to be fundamentally updated.
How Attackers Are Using AI and Chatbots
Hyper-Personalized Phishing at Scale
Traditional spear phishing, highly targeted attacks that incorporate personal details about the victim, has always been more effective than generic phishing but far more labor-intensive to execute. Generative AI eliminates that constraint. By feeding publicly available information about a target, LinkedIn profiles, company websites, press releases, social media activity, into a language model, attackers can generate highly personalized phishing emails in seconds, at the volume of bulk campaigns.
These messages reference real projects, use accurate job titles, reflect the recipient's actual professional context, and are written in fluent, professional language. They are significantly harder to identify as fraudulent, and significantly more likely to produce the credential submission, malicious link click, or wire transfer authorization that the attacker is seeking.
Automated Social Engineering via Chatbots
AI chatbots are increasingly being used to conduct real-time social engineering conversations, engaging targets in text or voice interactions that impersonate IT support staff, financial institutions, or trusted vendors. Unlike a static phishing email, an AI-driven chatbot can respond dynamically to the target's questions and objections, maintaining a convincing cover story across an extended conversation.
In some documented cases, attackers have deployed chatbots that initiate contact through legitimate-seeming customer support channels, collect verification information, and then use that information to bypass authentication controls at the actual institution being impersonated.
AI-Generated Malware and Exploit Code
Generative AI lowers the technical barrier for malware development. Code that previously required specialized expertise can now be generated, modified, and obfuscated with the assistance of AI tools, including commercially available models that have been jailbroken to bypass content restrictions. Attackers are using AI to produce malware variants that evade signature-based detection, generate novel exploit code for known vulnerabilities, and accelerate the development of attack tooling.
This has real implications for the speed of the threat landscape. The window between vulnerability disclosure and widespread exploitation is already shrinking. AI-assisted exploit development compresses it further. CyberSecOp's Vulnerability Management Service maintains continuous scanning and prioritized remediation workflows precisely because the time available to patch before exploitation is no longer measured in weeks.
Deepfake Audio and Video in Business Email Compromise
Business Email Compromise (BEC) fraud, in which attackers impersonate executives or financial officers to authorize fraudulent transactions, has been one of the most financially damaging forms of cybercrime for years. AI has introduced a new dimension to these attacks: deepfake audio and video that allows attackers to convincingly impersonate a CEO's voice or appearance in a phone call or video conference.
Reported cases include employees receiving audio calls from what they believed was their CEO, authorizing emergency wire transfers to attacker-controlled accounts. The audio was AI-generated using publicly available recordings of the real executive's voice. These attacks bypass the intuitive human check of 'I recognize this person's voice', historically one of the last lines of defense against telephone fraud.
Prompt Injection and Chatbot Manipulation
Organizations that deploy AI chatbots, for customer service, internal helpdesk, or productivity applications, face a distinct attack category: prompt injection. In a prompt injection attack, a malicious user crafts inputs designed to override the chatbot's instructions, bypassing safety guardrails, extracting confidential information from the model's context, or causing the bot to perform actions outside its intended scope.
For businesses that have integrated AI assistants with internal systems, databases, email platforms, CRM tools, a successful prompt injection can potentially expose sensitive data or trigger unauthorized actions within connected systems. As enterprise AI deployments expand in scope and integration depth, this attack surface grows proportionally.
AI-Powered Credential Stuffing and Account Takeover
Credential stuffing, using lists of stolen username and password combinations to gain unauthorized access to accounts, is not new. AI makes it significantly more effective by enabling adaptive attack strategies that adjust request timing, rotate user agents, and solve CAPTCHA challenges at scale. AI-driven credential stuffing tools can also intelligently prioritize credential lists, targeting the combinations most likely to succeed against specific platforms based on breach data analysis.
The Compounding Effect on the Human Layer
The most significant impact of AI-powered attacks is on the human element of security. Employees who are trained to spot phishing are trained to recognize patterns that AI increasingly masks. The grammatical errors, generic greetings, and implausible requests that characterized earlier phishing attempts are disappearing from AI-generated attacks. CyberSecOp's Security Awareness Training programs have been updated to address this shift, teaching employees to apply process-based verification rather than relying on textual cues that AI can now replicate convincingly.
This means verifying requests through secondary channels regardless of how legitimate they appear, applying strict authorization workflows for financial transactions and data access requests, and understanding that a well-written, contextually appropriate message is no longer evidence of legitimacy.
How MSSPs Respond to AI-Powered Threats
AI-Enhanced Threat Detection
Defending against AI-powered attacks increasingly requires AI-powered defenses. Behavioral analytics platforms that establish baseline patterns of user activity, and flag deviations consistent with account takeover, insider threat, or social engineering success, are far more effective against AI-generated threats than signature-based tools. An MSSP operates these platforms continuously, with analysts investigating and responding to alerts in real time.
Advanced Email Security and Anti-Phishing Controls
Modern email security platforms use machine learning to detect phishing attempts based on behavioral signals, sender reputation, content analysis, and link inspection, not just keyword matching. Deployed and managed as part of CyberSecOp's Managed Security Services, these controls are continuously tuned against the current threat landscape, including AI-generated content patterns that simpler filters miss.
Zero Trust and Strict Authorization Controls
The most effective structural defense against social engineering, AI-powered or otherwise, is reducing how much an attacker can accomplish even after successfully deceiving a human target. Zero Trust architecture limits lateral movement, enforces continuous authentication, and applies least-privilege access controls that contain the damage from a compromised account. When an employee is deceived into disclosing credentials, Zero Trust controls limit what those credentials can unlock.
Dark Web Monitoring for AI-Generated Fraud Signals
Criminal forums and dark web marketplaces are where AI-powered attack tools are developed, sold, and discussed. CyberSecOp's Dark Web Monitoring service tracks these sources for mentions of client organizations, exposed credentials, and emerging attack tooling, providing early warning of threats that have not yet been deployed.
Incident Response for AI-Assisted Attacks
When an AI-powered attack succeeds, a deepfake-assisted BEC fraud, a chatbot-driven credential harvest, or an AI-generated malware infection, the response requires both speed and forensic rigor. CyberSecOp's Incident Response Services are structured to address the specific characteristics of these attacks, including the challenge of distinguishing AI-generated artifacts from legitimate communications during forensic analysis.
vCISO-Level Strategic Oversight
The rapid evolution of AI-powered threats requires security strategy that keeps pace. CyberSecOp's Virtual CISO Program provides the ongoing strategic leadership to ensure that security programs, policies, and controls are updated in response to the changing threat landscape, not just after an incident forces the issue.
The Threat Will Continue to Evolve
Generative AI is improving rapidly, and the attack techniques enabled by it are evolving in parallel. The deepfakes of today are more convincing than those of last year. The phishing emails being generated now are more contextually accurate than those generated six months ago. Organizations that treat AI-powered threats as a future concern rather than a present reality are already behind.
A Cybersecurity Assessment from CyberSecOp will evaluate your organization's readiness for AI-powered threats across technical controls, employee awareness, and incident response capabilities. Contact us at cybersecop.com/contact to schedule a consultation with our team.

Why SMBs Should Use Virtual CISO (vCISO) Services from an MSSP
Small and mid-sized businesses face the same cyber threats as large enterprises — but rarely have the budget, headcount, or expertise to match. A Virtual Chief Information Security Officer (vCISO), delivered through a Managed Security Services Provider (MSSP), offers a practical and cost-effective path to enterprise-grade security leadership.
The Security Leadership Gap in Small Business
Cybersecurity is no longer a concern reserved for Fortune 500 companies. Today's threat landscape is indiscriminate — ransomware, phishing campaigns, supply chain attacks, and data breaches hit businesses of every size. According to industry research, 43% of cyberattacks target small businesses, and 60% of those businesses close within six months of a serious breach.
Yet for most SMBs, the question isn't whether to take security seriously. It's how to do so without the budget for a full-time C-suite security executive. Hiring a Chief Information Security Officer costs $180,000–$280,000 per year in salary alone, before benefits, bonuses, and the months-long hiring process. That's simply out of reach for most growing businesses.
This is where the vCISO model — delivered through an MSSP like CyberSecOp — becomes one of the most impactful decisions an SMB can make.
What Is a vCISO?
A Virtual Chief Information Security Officer is an experienced security executive who provides strategic leadership, program management, and compliance oversight on a fractional or on-demand basis. Unlike a full-time hire, a vCISO is available when you need them — scaling up during audits, incidents, or rapid growth phases, and scaling back during quieter periods.
Through CyberSecOp's Virtual CISO / vCISO Advisory Program, organizations receive a dedicated security leader who takes ownership of their security strategy without the overhead of a permanent executive headcount.
What a vCISO Does for Your Business
The decisions made in the early and mid-growth stages of a business — about data handling, vendor risk, access controls, and incident response — set the security posture for years to come. A vCISO takes responsibility for those decisions. Core responsibilities include:
Security program development: Building and maturing your security policies, procedures, and governance framework from the ground up — creating a program that grows with your business.
Risk assessment and management: Identifying your most critical assets and vulnerabilities through structured risk assessments, then prioritizing remediation based on business impact.
Regulatory compliance guidance: Navigating frameworks including HIPAA, PCI-DSS, SOC 2, CMMC, and NIST — managing documentation, control implementation, and audit readiness.
Incident response planning: Ensuring your business has a tested, documented plan before a breach — not scrambling to create one during an active incident.
Board and executive reporting: Translating technical risk into business language that leadership can act on, supporting informed decision-making at every level.
Vendor and third-party risk: Assessing the security posture of vendors, partners, and suppliers who access your data or systems.
Security awareness program oversight: Coordinating employee training programs that address the human element — the most common entry point for attackers.
In-House CISO vs. vCISO: The Real Comparison
For most SMBs, the idea of a full-time CISO sounds appealing in theory. In practice, the cost and operational overhead make it nearly impossible. Here is what the comparison looks like across the factors that matter most:
Annual cost: In-house: $180,000–$280,000+ in salary, benefits, and bonuses. vCISO: Fraction of the cost, scales with your needs.
Time to onboard: In-house: 3–6 month hiring cycle on average. vCISO: Operational within days to weeks.
Breadth of expertise: In-house: One individual's background and experience. vCISO: Entire MSSP team with cross-industry depth.
24/7 coverage: In-house: Rarely available outside business hours. vCISO: Yes, through integrated SOC monitoring.
Compliance knowledge: In-house: Varies significantly by candidate. vCISO: Multi-framework expertise built into the program.
Scalability: In-house: Limited by a single hire. vCISO: Scales up or down with business needs.
Continuity risk: In-house: High — departure creates an immediate gap. vCISO: Low — institutional knowledge is retained.
Why an MSSP-Backed vCISO Multiplies the Value
A standalone vCISO engagement gives you strategic leadership. A vCISO embedded within a full-service MSSP like CyberSecOp gives you something more powerful: an integrated security ecosystem.
Your vCISO has immediate access to threat intelligence, active monitoring capabilities, forensic investigation resources, and a team of practitioners who can execute the strategy they design. When a threat materializes at 2 a.m., the response isn't dependent on one person picking up a phone. It's backed by CyberSecOp's Incident Response Services and a dedicated Security Operations Center providing continuous monitoring and rapid containment.
When your vCISO is part of a broader MSSP structure, they seamlessly coordinate services like Vulnerability Assessments, Dark Web Monitoring, and Attack Surface Management — ensuring the security strategy is not just documented but actively enforced across your environment.
Compliance Without a Full-Time Hire
Regulatory compliance is one of the most common triggers for SMBs seeking vCISO support. Whether you're preparing for a SOC 2 audit, working toward CMMC certification for government contracts, or maintaining information security compliance standards, the documentation, evidence collection, and control implementation involved is substantial.
A vCISO through CyberSecOp takes ownership of that process — coordinating with your legal, IT, and operations teams to ensure security controls are implemented, tested, and documented in a way that survives an audit. They also advise on cyber liability insurance requirements, helping you qualify for coverage and negotiate better premiums by demonstrating a mature security posture.
Industry-Specific Security Leadership
Cybersecurity requirements for a healthcare organization subject to HIPAA look nothing like those for a law firm navigating client confidentiality or a financial services firm under SEC scrutiny. One of the strongest advantages of CyberSecOp's vCISO model is the depth of industry-specific expertise it brings to every engagement.
CyberSecOp's vCISO advisors bring vertical knowledge across sectors including Healthcare, Financial Services, Legal and Law Firms, Technology Companies, and Government Contractors. Each vertical carries distinct compliance frameworks, breach notification timelines, and threat profiles that a generalist security advisor simply cannot match.
Security Technology Stack Guidance
How a vCISO helps SMBs make smarter decisions about which security tools to buy, avoid, and retire, preventing the common trap of overspending on redundant tools or underinvesting in critical gaps. An in-house CISO may have vendor biases or limited exposure; an MSSP-backed vCISO brings cross-client visibility into what actually works.
Is a vCISO Right for Your Business?
A vCISO engagement deserves serious consideration if your organization recognizes any of the following situations:
You are subject to regulatory compliance requirements but lack dedicated security staff to manage them.
You have experienced a security incident — or near-miss — and need to understand your exposure and build a stronger defensive posture.
You are preparing for rapid growth, a merger, or a new enterprise client relationship that requires demonstrated security controls.
You have an IT team handling security reactively and need someone to build a proactive, strategic program.
You need to present a credible security posture to board members, investors, or insurance underwriters.
You are pursuing government contracts that require CMMC or other federal compliance certifications.
CyberSecOp's Cybersecurity Assessment Services are often the natural starting point — establishing your current security state before a vCISO engagement defines the roadmap forward. A Risk Assessment gives you and your vCISO a clear picture of where you stand, what is at risk, and where to focus first.
The Bottom Line
The cyber threat landscape does not distinguish between large corporations and small businesses. Attackers go where the vulnerabilities are — and SMBs without dedicated security leadership are disproportionately exposed.
A vCISO through CyberSecOp closes that gap. You get the strategic leadership of an experienced CISO, backed by a full MSSP infrastructure — at a fraction of the cost of a full-time hire, available from day one, and scaled precisely to your needs.
To learn more or schedule a consultation, visit cybersecop.com/contact or explore our full cybersecurity consulting services.